




Please note that timings may change.
We will continue to update the programme here so please check back frequently for updates or contact sara.hook@pulseconferences.com for the most recent draft programme.

10:00-10:30
LOBBY
PEOPLE
NETWORKING
EXPO
(30 mins)
Lobby – Check in and chat with peers!
People – Set up your virtual badge and profile, See who you know and who you don’t!
Networking – Ice-breaker CISO 360 Experience! Memorable 3-minute video connections with peers and luminaries!
Expo– Meet the Sponsors & Points for Prizes! Meet the sponsors, collect points at each stand to win prizes!
10:30-10:35
STAGE
(Video 5 mins)
Opening Remarks
Master of Ceremonies: Clive Room, Director, Pulse Conferences
10:35-10:40
STAGE
(Live 5 mins)
OPENING
Chairman’s Opening
Marcus Alldrick, CISO Luminary
10:40-11:10
STAGE
(Live 30 mins)
FIRESIDE CHAT
Looking Back, Looking Forward: Projects 2020 and 2030
In 2012, Vic and Rik built scenarios for the future of cybercrime. These became the basis for 2020, Trend Micro’s award-winning short movie series. Now that we’ve reached our time horizon and passed “Peak Blade Runner” last November, we’re reviewing how we did, and looking again to the future. In this short talk, we’ll take you through the original project and its results, and introduce you to the next generation of our work.
Rik Ferguson, Vice President Security Research, Trend Micro and Special Advisor, Europol
Dr Victoria Baines, Visiting Research Fellow, Oxford Department of International Development
11:10-11:35
STAGE
(Live 30 mins)
KEYNOTE

Do You Have Imposter Blindness? Fighting the Next Generation of Targeted Email Attacks
Simon Taylor, Information Security Manager, Stagecoach Group
Adenike Cosgrove, Cybersecurity Strategy, International, Proofpoint
11:35-12:00
STAGE LIVE
(Live 25 mins)
FIRESIDE CHAT
Next Generation Defence: Using Hackers to Beat Hackers
There are many dilemmas in today’s complex cybersecurity world. Year on year increases in cyber-attacks, an increase in the sophistication of these attacks, a widening cybersecurity talent gap, IT security budgets that haven’t kept up with growing demands, and now large remote work forces and social distancing requirements. In this fireside chat, Justin and Mark will discuss an innovative crowdsourced security model that has been deployed at Freshfields. Learn why Freshfields is utilizing an army of ethical hackers to harden their corporate assets; and how security operations have been transformed and simplified, all while quickly deploying safer applications.
Mark Walmsley, Chief Information Security Officer (CISO), Freshfields Bruckhaus Deringer LLP
Justin Shaw Gray, Director, Synack Inc.
12:00-12:15
NETWORKING & EXPO (15 mins)
Networking – CISO 360 Speed Networking Experience! Memorable 3-minute video connections with peers
Expo- Meet the Sponsors & Points for Prizes! Meet the sponsors, collect points at each stand to win prizes!
12:15-12:25
STAGE
(Video 5 mins)
CISO MUSE
Back to Basics – Why are the Basics STILL So Hard?
Quentyn Taylor, Director of Information Security EMEA, Canon Europe
12:25-12:55
STAGE
(Live 30 mins)
PANEL
Cyber Resilience in a VUCA world – What’s next? How do we translate trust, sharing and collaboration into technological terms?
Engaging the community with the big questions challenging leaders today. In a world of social media, false information, growing nationalism/authoritarianism, growing civil unrest and of course the current pandemic, hear predictions
· What is the current World order to cyber defence? How will this impact our businesses and economies?
· How we will find the right balance between legitimate increased surveillance for public health and intrusive mass surveillance?
• How can we ensure credible intelligence and increase levels of international collaboration?· Covid-19 is the greatest shock to business for a century. What will struggle to get back to how it was before, and what might change forever?
· What is the next killer digital virus, and will the world be able to cope with it?
· How can we mitigate the risks of and strengthen systemic resilience to fraud as critical priorities?
· What do the next generation of cybersecurity operations look like? What is the role of automation?
Chaired by: Professor Dr. Robert Coles, Visiting Professor, Royal Holloway, University of London
Joined by:
Graham Edwards, Head of Cyber Security, Yorkshire Water
Graeme Burnett Head of Application Security, Mastercard
Richard Hollis, CEO, Risk Crew
12:55-13:10
STAGE
(Live 15 mins)
KEYNOTE LIGHTNING TALK
Scams and Deception – Inside the mind of the scammer
We talk a great deal around the scam itself, but not about understanding the approach of individuals and why they scam. This session will take a very brief look into the factors that support why people commit deception related crime, and will look at the threats, challenges and responses to the changing fraud landscape. The demand for electronic devices to work and engage in social contact has substantially expanded the attack surface and the target pool has widened for fraudsters, who are also at the beginning of their own transformation!
Simon Scales, Specialist Public Sector SME and Former Head of Investigations
13:10-13:30
NETWORKING & EXPO (30 MINS)
Networking – CISO 360 Speed Networking Experience! Memorable 3-minute video connections with peers
Expo- Meet the Sponsors & Points for Prizes! Meet the sponsors, collect points at each stand to win prizes!
13:30-13:45
STAGE
(Live 15 mins)
KEYNOTE LIGHTNING TALK
What’s In Your Software?
Tracking the software and software components an organisation uses in its products and its operations is crucial for responding to emergency threats. However, building and maintaining these Software Bills of Materials (SBOMs) is very challenging, especially across large enterprises. In this session, Alyssa Miller discusses the hidden threats in the Software Supply Chain, and analyzes some of the unique challenges of open source software, IoT and Medical devices, and Industrial Control Systems. She’ll share real world strategies and risk mitigations that organizations should employ to address these threats and reduce the risks associated with them.
Alyssa Miller, Hacker/Researcher, Application Advocate, Snyk
13:45-14:25
STAGE
(40 mins)
FIRESIDE CHAT
CISOs, 5 questions – CISO Futurists: How can we take our strategy to the next level?
Chaired by: Kevin Fielder, CISO, Just Eat
Panellists:
Martyn Booth, CISO, Euromoney Institutional Investor PLC
Bev Allen, Head of Information Security Assurance, Quilter
14:25-14:55
THINK TANKS
(live 30 mins)
Truly Transformational! Sharing Practical Lessons
These CISO 360 Think Tanks provide the opportunity to benchmark lessons with peers and to hear tried and tested approaches to deal with four areas of security that are seeing rapid development. Working in smaller breakout groups for the roundtable discussions, gives you the opportunity to come face to face on screen. Return to Stage for the wrap up at the end! Understand: What role these technologies are expected to play; How these areas fit within the business risk strategy. These are not presentations but roundtable discussions.
PLEASE SELECT:
THINK TANK 1:
Future of Identity and Zero Trust
How are you ensuring the right individuals (or machines) access to the right resources, at the right times, for the right reasons?
Co-led by: Mike Kiser, Global Strategist and Evangelist, Office of the CTO, SailPoint
Karl Lankford, Director, Solutions Engineering BeyondTrust

THINK TANK 2:

CyberOptimise360
How are we streamlining or optimising our cyber programmes?
Co-led by: Scott Raspa, Director and Jesse K. Dean, Vice President, Solutions, TDI
THINK TANK 3:
CISO-DevSecOps
How can we develop secure and fast.
Led by: Alyssa Miller, Hacker/Researcher, Application Advocate, Snyk

THINK TANK 4: 
Cloud Security Risks and Audit
Mitigations, audit, compliance in cloud.
Led by: Mike Milner, Global Director of AppSec Technology, Trend Micro & CTO/Co-founder of Immunio
14:55-15:10
STAGE (15 mins)
WRAP UP
Truly Transformational – Wrap Up
Think Tank leaders have 3 minutes per Think Tank to share key findings back to the group, to wrap up.
15:10-15:25
NETWORKING & EXPO
(15 mins)
CISO 360 Speed Networking Experience! Memorable 3-minute networking to connect with CISO peers!
Meet the Sponsors & Password to Prizes! Meet the sponsors, find the password at each stand to win prizes!
15:25-15:30
STAGE
(5 mins)
CISO MUSE
A Better Way of Collaborative Working with Security
Martyn Booth, CISO, Euromoney Institutional Investor PLC
15:30-16:15
STAGE
(45 mins)
VIRTUAL FISHBOWL

Cyber Culture: Controls, Continuity and Compliance
The Fishbowl (main speakers) introduce and discuss the issues, while the outer circle participants observe the discussion, moving in and out of the Fishbowl, at the invitation of the Chairman, to share experiences and to ask questions. We look forward to an energised discussion! If you would like to be in the fishbowl participant observer partaking on screen please let us know at teampulse@pulseconferences.com!
Chaired by: Professor Dr. Robert Coles, Visiting Professor, Royal Holloway, University of London
Fishbowl Speakers:
Amy Lemberger, Information Security Director, Gamma
Dr. Vasileios Karagiannopoulos, Institute of Criminal Justice Studies, University of Portsmouth
Tim Ward, Director, Think Cyber Security Ltd
Steve Collins, Head of IT Security, First Quantum Minerals
James Kwaan, President, (ISC)2 Scottish Chapter
+Fishbowl Participants ‘Outer Circle Observers’
16:15-16:50
ZOOM
(30 MINS)
ROUNDTABLES
Sharing operational best practices with peers
What keeps you up at night in terms of data security threats?
Peer to peer discussion led by: Simon Hill, Chief Legal & Compliance Officer, Certes Networks
Securing Data & Privacy in a Remote Workforce – Best Practices & Controls
Continue the fish bowl discussion with peers face to face for an in-depth exchange! Focus on sharing on new frameworks, monitoring and collaboration strategies.
Peer to peer discussion led by: Toby Hayes, Global Data Protection Controller, Pladis Global
Cyber Threat Intelligence Landscape
Sharing operational best practices on cyber threat intelligence.
Peer to peer discussion led by: Richard Hollis, CEO, Risk Crew
16:50-17:25
STAGE (35 mins)
KEYNOTE
WFH
Michael Colao, Chief Corporate Security Officer, AXA
17:25-17:35
POINTS FOR PRIZES
& CLOSE
Points for Prizes – Winners Announced! Summaries and Close
Master of Ceremonies: Clive Room, Director, Pulse Conferences and Marcus Alldrick, CISO Luminary
17:35-17:50
NETWORKING & EXPO
(15 MINS)
Last Chance Networking – CISO 360 Speed Networking Experience! Memorable 3-minute video connections with peers
The ultimate sound-boarding for today’s cybersecurity leaders. Guests are expected to contribute to the discussions that will be held under The Chatham House Rule.
Pre-event:
You shape the topics by inputting your top 3 current priorities.
On the day:
The size and interests of the group will determine if break out rooms are required.
Participants are invited to contribute to the discussion and to be visible on screen if you are comfortable to do so.
Post-event:
Output report (non-attributed as to who said what)
10:00 -10:10
Guest Introductions and Chairman’s Opening
10:10-11:30
#CISO 360 Roundtable
Chaired by: Professor Dr. Robert Coles, Visiting Professor, Royal Holloway, University of London
Co-Facilitated by:
11:30
Wrap Up and Close of Roundtable

Marcus Alldrick, CISO Luminary
Born at a very early age and growing up in a culture where cyber was a prefix for anything automated, menacing and malevolent (how history has a tendency of repeating itself), Marcus entered the world of Data Processing as it was known back then after graduating from university. Progressing from programming into analysis and then data architecture Marcus became the first devolved Information Risk and Security Manager for Barclaycard. After seven years in that role he moved banks and became Head of Information Security for Abbey National plc, now Santander UK. After six years at Abbey and a move into consulting for a large UK utilities company Marcus joined KPMG as a Principal Advisor. Eighteen months later he joined Lloyd’s of London as its CISO and subsequently became its Head of Digital Risk Management and Compliance, also embracing responsibility for data protection and privacy, during his 10 years tenure there. Having worked in IT for over 40 years, specialising in information risk, protection, security and compliance for the latter 27 years or so, Marcus decided to leave full-time corporate life and move to the South Coast of England in mid-2017, ever the seafaring Fisherman’s Friend. As well as being a proud member of the Pulse Conferences family, Marcus now provides pro bono advisory and volunteering services and is a guest lecturer at the University of Portsmouth.
We are always looking for:
We welcome your input into shaping the agenda and speaker panels.
Our programmes are highly researched with practitioners who do the job day in and day out. They are organic to ensure that we remain agile to meet the most current requirements.
For further information, please contact Sara Hook
+44 (0)20 7936 8989 or sara.hook@pulseconferences.com

Information Security Director, Gamma
Amy Lemberger is the Information Security Director at Gamma Group, responsible for data security and governance. Amy has a proven track record designing, implementing and leading security teams for large organisations. Including: • Security Operations Centre (SOC), • Cyber Security and Incident Response Teams (CSIRT), • Security Training and Awareness • Transformation teams.
Prior to joining Gamma Amy was the Cybersecurity Director at the GSM Association (GSMA), supporting their membership improve the security posture of the mobile telecommunications ecosystem and a Head of Security at BT, developing their incident response (IR) and digital forensics strategy. Amy is a delivery driven security professional who goes the extra mile, often challenging the status quo to innovate within her area of responsibility. Extensive professional development and cross industry exposure means she is able to articulate current threats against modern business risks, including effective ways to address them. Amy is currently studying her MBA (Tech Mgt) with the Open University. In 2008 she graduated with a First Class (hons) degree in Digital Forensics and holds various current industry certifications including CISSP, CISM, GNFA and EnCE.

Hacker/Researcher, Security Advocate, Application Advocate, Snyk
Alyssa Miller (CISM) is a life-long hacker, security advocate, author, and public speaker with almost 15 years of experience in security roles. She has always had a passion for deconstructing technology, particularly since buying her first computer at the age of 12 teaching herself BASIC programming. In her career, Alyssa has performed all forms of security assessments but given her developer background, she has a dedication to application security. She specializes in working with business and security leaders to design and deploy effective security programs that strengthen enterprise security posture. Alyssa is also committed to advocating for improving security practices. Not only does she speak internationally at various industry, vendor and corporate events, Alyssa also engages in the community through her online content, media appearances, and security community activism. Her journey through security was recently featured in Cybercrime Magazine. She’s also been recognized in Peerlyst’s e-Book “50 Influential Penetration Testers”. Alyssa is board member for Women of Security (WoSEC), Advisory Board Member for BlueTeam Con, and serves on the review board for DevSec Con. She is currently an Application Security Advocate for London-based Snyk Ltd.

Cybersecurity Strategy, International, Proofpoint
Adenike Cosgrove is the Cybersecurity Strategist for international markets at Proofpoint, where she drives product marketing strategy across European and Asia Pacific markets. She provides expertise on key regional cybersecurity strategies such as people-centric security, risk management, data privacy, and compliance.

Vice President, Solutions, TDI
Jesse K. Dean, CISSP, PMP has over 20 years’ experience in cybersecurity and IT. His career in cybersecurity began in 2003 in support of a preeminent law enforcement agency and expanded during his ten years at Booz Allen Hamilton, where as a Sr. Associate he consulted for dozens of U.S. defense and civilian agencies in the areas of cybersecurity policy, audit, and compliance. Jesse transitioned in 2014 to General Dynamics (GDIT) where in his new role, he led large IT infrastructure projects in healthcare to include on-prem and AWS cloud which supported several critical White House initiatives around affordable care, his program winning the FedHealthIT Award for innovation. Jesse is currently at TDI, a Washington, DC based cybersecurity firm where he’s been focused on innovative ways CISO’s can measure and improve cybersecurity performance and do more with less. He holds a Master’s in Information Technology, with a concentration in Information Systems Project Management from the George Washington University. https://www.linkedin.com/in/dc-jkdean/ (email jesse.dean@tdisecurity.com)
Head of Application Security, Mastercard
Head of Cyber Security, Yorkshire Water
President, (ISC)2 Scottish Chapter

Director, Synack Inc.
Justin Shaw-Gray is the Sales Director for the UKI region for Synack, Inc. In 2018, shortly after joining Synack, Justin was awarded SC Media’s Runner Up for Best Cybersecurity Sales Leader. Prior to Synack Justin held senior roles at Netscope, Zscaler, and Riverbed. Justin is originally from Zimbabwe where he was Founder and Human Rights Activist for the Restoration of Human Rights Zimbabwe. Justin is an avid runner and lives in London with his wife and three young children.

Solutions Engineering. BeyondTrust
Karl Lankford is the Director, Solutions Engineering, for BeyondTrust, where he has worked for 6 years. A highly capable security leader, Karl has acquired a wide range of security experience and knowledge over the last decade, working across multiple industries. Karl is a regular speaker at industry conferences, delivering disruptive technical and strategic thought-leadership insight to the international cybersecurity community.

CISO, JustEat
Innovative and dynamic security professional, with a passion for driving change by successfully engaging with all levels of the business.
I am a determined individual with proven ability to provide security insights to the business, in their language. These insights have gained board buy in for delivering security strategy aligned to key business goals. This is achieved by understanding the need to drive change through people, process and technology, rather than focusing exclusively on any one area. I take pride in being a highly articulate, motivational and persuasive team-builder. I have a strategic outlook with the ability to engage with and communicate innovative and effective security solutions to all levels of management. Along with a proven ability to translate security into business language and articulate the business benefits I am also passionate about leading security innovations and making security a key part of the business proposition to its customers. Security should be made a key differentiator to drive sales and customer retention, not just a cost centre! As a final note, all posts, articles, comments etc I make on LinkedIn are personal and do not necessarily represent the opinions of my employer(s).
https://twitter.com/kevin_fielder for more general musings. @kevin_fielder on Instagram for mostly fitness and daddy/daughter posts 🙂

CISO, Signify
Mark has more than 20 years of experience in the information security and information risk management, from technical roles to his recent role as a CISO for Signify (formerly Philips Lighting). He holds a Master of Information Management degree, believe in a business-driven approach to managing information risk, and is always willing to experiment with new ideas to improve our profession.
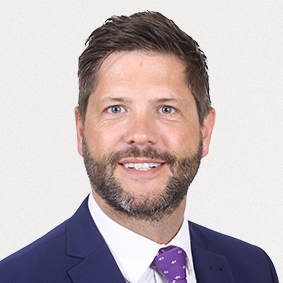
Chief Information Security Officer (CISO), Freshfields Bruckhaus Deringer LLP
Mark Walmsley is an experienced chief information security officer. He studied law before joining a number of small boutique private investigation agencies. The majority of Mark’s professional career has been spent within the legal industry, working within litigation before moving to business services where he managed high-value, complex programmes of work. Over the past year and a half Mark has had a part-time secondment to the National cyber Security Centre (part of GCHQ) where he helped manage the government and legal industry engagement.

CISO, Euromoney
Martyn is an experienced information security leader, working at board level to define information security strategy and then manage teams to implement that strategy. Martyn works with clients in a flexible and proactive way to meet stringent security requirements and adaptive needs, enabling businesses to work in a flexible way by reactively designing security processes and technical controls that support the business rather than inhibit it. Specialties: Risk, Compliance, Governance, Awareness, Security Architecture, application architecture, CLAS, .NET, Java, Online Piracy, Digital Economy Act, Firewalls, Security, Networks, Windows, ISO 27001, PCI DSS, policy

Chief Corporate Security Officer, AXA
Michael has been the head of security for AXA in the UK for more than five years. Prior to that he was a director of Downtown Associates, an information security and privacy consultancy, where he assisted firms in the Lloyd’s Insurance market. Previously to that he was the Global Head of Information Security as well as the Global Head of Privacy and Data Protection for the investment bank Dresdner Kleinwort, Michael has a strong side-interest in computer forensics and in the management of digital evidence. He graduated from the Massachusetts Institute of Technology in 1987 where he studied Mathematics and Computer Science. He has since lived in three continents and has lectured globally on security technology issues. Since 1996 has been working in Security and Technology in Financial Services in London.

Global Strategist and Evangelist, Office of the CTO, SailPoint
Mike Kiser is insecure. He has been this way since birth, despite holding a panoply of industry positions over the past 20 years—from the Office of the CTO to Security Strategist to Security Analyst to Security Architect—that might imply otherwise. In spite of this, he has designed, directed, and advised on large-scale security deployments for a global clientele. He is currently in a long-term relationship with fine haberdashery, is a chronic chronoptimist (look it up), and delights in needlessly convoluted verbiage. He has been a speaker on topics ranging from identity governance to security analytics, network security, and various related privacy issues, and is the co-host of a podcast illuminating all things identity. He warmly embraces the notion that security is more of a state of mind than a destination.

Global Director of AppSec Technology, Trend Micro & CTO/Co-founder of Immunio
Director of AppSec Technology at Trend Micro Inc. Product design and direction to ensure that Trend Micro’s Application Security products solve real pain points and provide solutions that delight customers. Works with Trend Micro sellers, sales engineers, marketing, industry analysts, partners, and other internal and external stakeholders to successfully launch new products to market. Extensive background working in the law enforcement and national security space in Canada and the UK, working across government and industry to leverage technology to enable new capability. Constantly driven to solve problems. As technology advances, new opportunities emerge to solve new problems, and new problems emerge in the technology itself. This fertile environment encourages the disruption and innovation I relish. When not working, I enjoy time with my wife and two kids, at home and outdoors – whether skiing in the hills, hiking and camping in the woods, or diving underwater.

Director of Information Security EMEA, Canon Europe
Quentyn has a wealth of experience in both the IT and information security arenas and, in recent years, has focused his attention on building business relationships across the world. Quentyn has driven Canon’s strategy to highlight the importance of document security and help business customers to minimise their security risk. Quentyn strongly believes in educating users about the importance of a comprehensive, overall security framework that will allow Canon’s business customers to improve security in a cost-effective way. During his career, Quentyn has worked in a variety of industries for a number of organisations including outsourced service providers, Internet service providers as well as Dotcom businesses, before moving to Canon in 2000.

CEO, Risk Crew
Professional information security governance, risk & compliance consultant with over 30 years of hands on skills & experience in:
• Threat Assessments & Risk Analyses
• Supply Chain Information Risk Management
• Information Security Policies & Procedures
• Security Vulnerability Assessments
• Security Penetration Testing
• Advanced Persistent Threats
• Wi-Fi Security Assessments
• Cloud Security Assessments
• Mobile Device Security
• Insider Threat & Data Leakage
• Security Awareness Training

Vice President Security Research, Trend Micro and Special Advisor, Europol
Rik is a Special Advisor to Europol EC3, project leader with the International Cyber Security Prevention Alliance (ICSPA), Vice Chair of the Centre for Strategic Cyberspace & Security Science and advisor to various UK government technology forums. In April 2011 Rik was inducted into the Infosecurity Hall of Fame. As a presenter at global industry events such as RSA, Mobile World Congress, InfoSecurity, Virus Bulletin, RUSI and the e-Crime Congress, Rik addresses the challenges posed by emerging technology and online crime. He is frequently interviewed by the BBC, CNN, CNBC, Channel 4, Sky News and Al-Jazeera English and is quoted by national newspapers and trade publications throughout the world. Rik writes the Countermeasures blog and is the lead spokesperson for Trend Micro, he also writes regular columns for CIO, ZDNet, T3 and several other European publications. In this position, Rik is actively engaged in research into online threats and the underground economy. He also researches the wider implications of new developments in the Information Technology arena and their impact on security both for consumers and in the enterprise.

Director, Tetrad Digital Integrity (TDI)
Scott is the Director at TDI for their CnSight product. Scott has 16+ years of sales and marketing experience and several years of experience working in the cybersecurity space. Prior to TDI, Scott worked with cyber analytics firm, IKANOW, and phishing defense firm, Graphus.

Specialist Public Sector SME and Former Head of Investigations
Simon has over 30 years significant investigative, security and compliance related experience, formed from an extensive corporate and law enforcement background. He is recognised for having conducted complex Bribery, Corruption, Fraud and Misconduct investigations worldwide, in regulated and non-regulated arenas. He is internationally recognised for his public speaking credentials and his vast experience, having successfully led, directed and managed investigation, ethics, compliance and integrity teams within Europe, the USA, Africa and the Middle East. He has also been instrumental in delivering investigative services to the key emerging markets of South America, India and China.

Chief Legal and Compliance Officer, Certes Networks
As Legal Counsel for Certes Networks, Simon assists with regulatory and compliance issues, contract drafting and negotiations, disputes, intellectual property and general legal matters. Simon has extensive international experience as a technology lawyer, working in multiple jurisdictions including the European Union, Japan, India and the United States for clients in both government and private sector. Simon is a regular speaker on data protecting regulations including GDPR, HIPAA and PCI DSS. Simon resides in Pittsburgh, Pennsylvania.
Head of IT Security, First Quantum Minerals

Director, Cumberland House Consulting Ltd, Honorary Professor, UCL and Visiting Professor, Royal Holloway, University of London
Professor Dr. Robert Coles is a Visiting Professor at Royal Holloway, University of London, where he is conducting his research into security culture change. He also runs his own consulting business. Prior to this, Robert was the first Chief Information Security Officer at GSK from 2013 to 2018. Robert held several CISO roles prior to joining GSK. He was the first CISO at National Grid and Merrill Lynch before that. In all these roles, he owned the information security risk and was responsible for providing global leadership. He was accountable to the Executive and PLC Boards for establishing information security strategy and direction. Building global information security capabilities and overseeing all of the information security initiatives across the organisations has been his primary career focus. Robert has been working in the field of Information Security for over 30 years, including “head of” roles at Royal Bank of Scotland, and the lead partner in KPMG’s Information Security Services for EMEA. Robert has extensive links with major industry information security networking groups and government security agencies. He also has links with a number of universities and participates in leading edge research, particularly with Royal Holloway where he is an Executive Sponsor for the Institute of Information Security Innovation, and Cranfield University where he is a External Advisory Board member. He was awarded a PhD in psychology at the University of Leeds in the perceptions of information and IT risk and has published and presented on this and other topics.

CEO and Co-Founder, Think Cyber Security Ltd
Tim is CEO and Co-Founder (with Dr Mike Butler) of Think Cyber Security Ltd. An organisation that is driving the next generation of security awareness. Their products embed awareness training into the day-to-day user experience, drawing on Behavioural Psychology and “Nudge” theory to create enduring behaviour change. Tim posts daily on LinkedIn on topics of behaviour change and security awareness. Tim has worked in IT and security for more than 20 years both in consulting and corporate with organisations including Logica, PA Consulting, Sepura and was previously Global Head of Information Services for the cyber division of BAE Systems (previously known as Detica). Tim studied Computer Science with AI at the University of Leeds, holds an MBA from the Open University and a Post Graduate Diploma in Entrepreneurship from Cambridge University.

Global Data Protection Controller, Pladis Global
With 17 years of experience in privacy and data protection, Toby is known for developing pragmatic and innovative privacy management solutions within commercially and technically complex environments, delivering best of breed risk management against tight deadlines, whilst remaining flexible to support business objectives. Prior to taking over the DPO role for pladis, Toby worked with clients in the UK, Europe, Far East and Australia for technology, government and financial services organisations including the likes of Carnival UK, Mitie, Post Office, Royal Mail and the Government Digital Service (GDS). As an experienced trouble-shooter for challenging identity and privacy strategies, his clients’ high-profile projects included GOV.UK Verify, the National Identity Scheme, E-Borders and Road User Charging. A regular conference speaker and media interviewee, he authored the Information Commissioner’s Privacy by Design strategy, served on the International Association of Privacy Professionals’ European Advisory Board, is a former Chair of the BCS Information Privacy Expert Panel, and sits on the Cabinet Office Privacy & Consumer Advisory Group (PCAG). Focus: GDPR, Data Protection, Privacy Impact Assessment (PIA) / Data Protection Impact Assessment (DPIA), Privacy by Design, Privacy Shield, Identity Assurance, Information Security, Risk Management, Governance, Training, Public Speaking, Business Development

Visiting Research Fellow, Oxford Department of International Development
Dr Victoria Baines is a leading authority in the field of online trust, safety and cybersecurity. She regularly contributes to the BBC, CNN and other major broadcast media outlets on digital ethics, cybercrime and the misuse of emerging technologies, including Virtual Reality. Her areas of research include electronic surveillance, the changing face of online identity, and the politics of security. In 2019, she was recognized by Secure Computing magazine among the top 50 women of influence in cybersecurity. She is co-host of the award-nominated Cyber Warrior Princess podcast, demystifying security issues for a popular audience. For several years Victoria was Facebook’s Trust & Safety Manager for Europe, Middle East and Africa. Her work focused on operational support to law enforcement, and strategic engagement with policy makers on criminal activity online. Before joining Facebook, Victoria led the Strategy team at Europol’s European Cybercrime Centre (EC3), where she was responsible for the European Union’s cyber threat analysis. She designed and developed the iOCTA, the EU’s flagship threat assessment on cybercrime, and authored 2020, scenarios for the future of cybercrime that were the basis for an award-winning short film series of the same name. She also led the Virtual Global Taskforce’s threat assessments on online child exploitation, and the analytical arm of the European Financial Coalition against commercial sexual exploitation of children online. Prior to this, Victoria was Principal Analyst at the UK Serious Organised Crime Agency (SOCA), the forerunner of the National Crime Agency. There she was responsible for the UK’s threat assessment of online child exploitation and abuse, and authored global law enforcement’s contribution to the 2008 World Congress against the sexual exploitation of children. She began her career in law enforcement in 2005 as a Higher Intelligence Analyst for Surrey Police. In 2008, the International Association for Law Enforcement Intelligence Analysts recognised Victoria’s work with an award for outstanding achievement. Victoria serves on the Advisory Boards of cybersecurity firm Reliance ACSN and the International Association of Internet Hotlines (INHOPE), and is a trustee of the Lucy Faithfull Foundation. She is a graduate of Trinity College, Oxford and holds a doctorate from the University of Nottingham, UK. She is a Visiting Fellow at Oxford University’s Department for International Development, Bournemouth University’s School of Computing, and the Stanford Internet Observatory.

Institute of Criminal Justice Studies, University of Portsmouth
Dr Karagiannopoulos holds an LLB from Athens Law School and an LLM in Information Technology and Telecommunications Law and a PhD in Law from the University of Strathclyde, School of Law. He has taught Information Technology Law, Intellectual Property Law, E-commerce Law and Human Rights Law for Strathclyde and Edinburgh Law Schools and is now a Senior Lecturer in Law and Cybercrime working for the Institute of Criminal Justice Studies (ICJS), University of Portsmouth. Vasileios has designed and is the course leader for the new ICJS BSc in Criminology and Cybercrime. He is also the Director of the Portsmouth Cybercrime Awareness Clinic, a project working with SMEs and vulnerable populations to increase cyberawareness and build resilience to cybercrime through research and public engagement activities. Vasileios is also an IISP Certified Forensic Investigations Practitioner and a member of the Institute for Ethical AI and Machine Learning. He has published in UK and US peer-reviewed journals on the topics of computer misuse law and insider unauthorised access, social media and the Arab Spring and also Internet regulation in China. His monograph by Palgrave Macmillan, Living with Hacktivism: From Conflict to Symbiosis, focuses on hacktivism and discusses the challenges faced by the US and UK criminal justice systems when dealing with such phenomena.
Proofpoint is a leading cybersecurity company that protects organizations’ biggest risks and greatest assets: their people. With an integrated suite of cloud-based threat, information and user protection solutions, we help organizations around the world mitigate their most critical security and compliance risks. More than half of the Fortune 100 trust us to stop targeted threats, safeguard their data, and make their users more resilient against cyber attacks. No one protects people, the data they create, and the digital channels they use more effectively than Proofpoint.
SailPoint: Rethink Identity
SailPoint, the leader in identity management, delivers an innovative approach to securing access across the enterprise with the SailPoint Predictive IdentityTM platform. With SailPoint, enterprises can ensure that everyone and everything has the exact access they need, exactly when they need it, intuitively and automatically. Powered by patented Artificial Intelligence (AI) and Machine Learning( ML) technologies, the SailPoint Predictive IdentityTM platform is designed to securely accelerate the business while delivering adaptive security, continuous compliance and improved business efficiency. As an identity pioneer and market leader serving some of the world’s most prominent global companies, SailPoint consistently pushes the industry to rethink identity to the benefit of their customers’ dynamic business needs.
Stay up-to-date on SailPoint by following us on Twitter and LinkedIn and by subscribing to the SailPoint blog.
Checkmarx is the Software Exposure Platform for the enterprise. Over 1,400 organizations around the globe rely on Checkmarx to measure and manage software risk at the speed of DevOps. Checkmarx serves five of the world’s top 10 software vendors, four of the top American banks, and many government organizations and Fortune 500 enterprises, including SAP, Samsung, and Salesforce.com. Learn more at Checkmarx.com or follow us on Twitter: @checkmarx.
BeyondTrust is the worldwide leader in Privileged Access Management (PAM), empowering organizations to secure and manage their entire universe of privileges. Our integrated products and platform offer the industry’s most advanced PAM solution, enabling organizations to quickly shrink their attack surface across traditional, cloud and hybrid environments.
The BeyondTrust Universal Privilege Management approach secures and protects privileges across passwords, endpoints, and access, giving organizations the visibility and control they need to reduce risk, achieve compliance, and boost operational performance. Our products enable the right level of privileges for just the time needed, creating a frictionless experience for users that enhances productivity.
With a heritage of innovation and a staunch commitment to customers, BeyondTrust solutions are easy to deploy, manage, and scale as businesses evolve. We are trusted by 20,000 customers, including 70 percent of the Fortune 500, and a global partner network.
Synack, the leader in crowdsourced security testing, helps organizations protect themselves from cyber attacks. By leveraging the world’s best ethical hackers and an AI-enabled platform, Synack helps organizations find and fix critical security issues and provides valuable security intelligence on digital assets. The Synack platform delivers data-driven insights to help organizations understand their risk from a hacker’s perspective and then mitigate that risk with a hacker’s help. These insights secure critical infrastructure and leading brands and businesses around the world- Synack protects leading global banks, DoD classified assets, and close to $1 trillion in Fortune 500 revenue. For more information visit us at www.synack.com
Risk Crew is an elite group of product-independent, information governance, risk, and compliance management professionals. We’re the forerunners in the design and delivery of effective business information and communication technology risk and security solutions. We understand business risk and compliance and so we also excel in the creation of operative controls and processes to cost-effectively comply with legislation, regulation and best commercial practices such as the Payment Card Industry (PCI), Data Security Standards (DSS), the UK Data Protection Act (DPA) and ISO/IEC 27001. Risk Crew take great pride in the depth and breadth of our technical and tactical knowledge and will work to ensure that it’s fully leveraged to provide the greatest benefit to your business objectives. We also put skin in the game and guarantee all of our services. Consequently, we are the selected supplier of choice for hundreds of businesses in virtually every commercial sector across the United Kingdom. www.riskcrew.com
Snyk is a developer-first security company that helps software-driven businesses develop fast and stay secure. Snyk is the only solution that seamlessly and proactively finds and fixes vulnerabilities and license violations in open source dependencies and container images. Snyk’s solution is built on a comprehensive, proprietary vulnerability database, maintained by an expert security research team in Israel and London. With tight integration into existing developer workflows, source control (including GitHub, Bitbucket, GitLab), and CI/CD pipelines, Snyk enables efficient security workflows and reduces mean-time-to-fix. For more information or to get started with Snyk for free today, visit https://snyk.io
TDI’s journey began in 2001 with a dream to provide the best in cybersecurity and has grown into a world-class consulting firm offering innovative services and solutions to government agencies and commercial clients around the world. After 20 incredible years spent perfecting cybersecurity professional services, engineering, and consulting, TDI has captured and automated our know-how in the CnSight platform. CnSight is a breakthrough cybersecurity solution that provides automated Cyber Risk, Effectiveness & Performance Management insights to security and business leaders who want to mature their security programs. It’s lightweight and first of its kind, capable of ingesting data from anything to provide cyber situational awareness, continuous monitoring, risk and vulnerability management, metrics tied to business objectives, executive-level analytics and visualization on the effectiveness of cyber programs, and much more. CnSight automatically manages risk by effectively measuring cyber performance and maturity, transforming an organization’s tools, goals, and assets into attributable KPIs and actions.
Visit https://www.tdisecurity.com/, https://twitter.com/tdisecurity, https://cnsight.io/
Certes Networks Provable Security™ introduces a new way to think about data security and the effectiveness of an organization’s security strategy. Based on the Certes Five Pillars, or key performance indicators (KPIs), we offer features that are quantifiable, measurable and outcomes driven. Our encryption management solution delivers on these KPIs and is able to quantify the network security role to build, modify and measure a security strategy that aligns and protects the needs of the organization while preventing data breaches and mitigating risk.
Headquartered in the U.S. with a global presence in Europe, Middle east and Asia Pac, Certes Networks has been delivering data security technology solutions to enterprises and governments around the world for over 15 years. Our technology is deployed across 1000 customers in nearly 100 countries and is certified for FIPS 140-2 and Common Criteria EAL4+. Our global footprint of organizations using Certes technology has helped customers to meet national, international and industry-specific regulations.
For over 30 years, Trend Micro’s unwavering vision has been to make the world safe for exchanging digital information. Security is our entire focus, and it shows. This single-minded passion has inspired our innovations that keep up with the bad guys despite a changing IT landscape, riskier user behavior, and constantly evolving threats. The depth of our experience remains unmatched. From the endpoint to the network to the cloud, we’ve got you covered with a connected threat defense recognized by analysts, customers, and industry gurus of all kinds.
Barclay Simpson is a specialist international corporate governance recruitment company providing contingent and retained permanent recruitment solutions and interim contract services. Our consultants, based in our offices in London, and New York work with our clients throughout the UK, Europe, the Middle East and North America. We recruit for a wide range of leading commercial, banking, financial services, professional services and public sector organisations. We specialise in recruiting for the distinct but interrelated disciplines of Internal & IT Audit; Risk Management; Compliance; Security & Resilience; Legal and Treasury. www.barclaysimpson.com
 “Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” Europe Industries- Security Officer, Air Liquide GMS“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” Technology Services Head of Cyber Security, DWP
 “A very thoughtful event, great networking and industrial expertise in the room to learn from!” Ryan Chan, Director, Security, Laureate International Universities Malaysia“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” SailPoint“If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85 “Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85

 “Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with

Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh
— Holly Foxcroft (@holly_foxcroft) 21 June 2018
“A very engaging, varied and interactive event. The best conference I have ever attended!”“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group “Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, EuronextIt was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO— Viktor Polic (@ViktorPolic) 26 June 2018
“The best speaker line-up of any security conference in Europe!”“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon EuropeSad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !
— Quentyn Taylor (@quentynblog) 21 June 2018
“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz
— Quentyn Taylor (@quentynblog) 21 June 2018
“Refreshing views of security topics for knowledge improvement!”““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo
— avatao (@theavatao) 21 June 2018
High quality 60mins #CISO360 @mikko pic.twitter.com/khkIJhzsBB
— Jonathan Luff (@jjluff) 20 June 2018
“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint “”I found CISO 360 Congress a great place to share ideas about current and future problems”“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”““Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”““Excellent conference, brilliantly put together.”Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!
— Jonathan Luff (@jjluff) 20 June 2018
Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC
— Dr Victoria Baines (@cyberbaines) 21 June 2018
Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv
— AP2SI (@AP2SI) 22 June 2018
“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!” Corporate Security Manager, Logista“Marvellous event, well-run, packed with useful content you can use”, Technology Services Head of Security, DWP