https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-asia-oceania-01.jpg
https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-asia-oceania-02.jpg
https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-asia-oceania-03.jpg
https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-asia-oceania-04.jpg
https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-asia-oceania-05.jpg
https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-asia-oceania-06.jpg
https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-asia-oceania-07.jpg
https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-asia-oceania-08.jpg
CSO 360 Asia and Oceania · co-located with the 6th CISO 360 Asia and Oceania
Corporate Security Leadership: Resilience as a Strategic Business Advantage
Peer-led discussion and case stories for chief security officers and corporate security leaders across Asia and Oceania.
The event will unite leaders in security, intelligence, resilience, and investigations from across the APAC region.
✔ Engage in a global dialogue on resilience – Explore solutions to today’s most pressing challenges
✔ Broaden perspectives – Collaborate with top security professionals and learn trust-based tactics to build business resilience
✔ Unique security cross-pollination opportunity – Parts of the agenda and the evening networking will seamlessly bridge CSO 360 Asia & Oceania with the co-located 5th CISO 360 Asia & Oceania, creating a unique gathering for directors of corporate security and cybersecurity to network and learn from one another.
Inspiration, tools, and actionable insights will be shared from peers and experts, fostering resilience in a rapidly changing landscape.
Register now for CSO 360 Asia & Oceania!
Raising the Resilience Bar! Two conferences, one location. Together but apart.
Attending? Help us spread the word- Download one of our I am attending banners and post on your social channels!
Banner CSO | Banner CISO & CSO
/uploads/2025/12/Anchor-Partners-2025-Banner-for-all-sites.png)
/uploads/2025/01/International_SOS_NEW.jpg)
/uploads/2025/05/enteles-search.png)
/uploads/2025/01/International_SOS_NEW.jpg)
/uploads/2024/01/1._High_Res_-_Chapter-logo-Rebrand-APAC_Region_Page_073-removebg-preview.png)
/uploads/2025/12/WiCyS.jpg)
The 2027 Agenda is currently in development.
View the past agenda - 2026The 2027 programme is currently being developed. If you would be interested in getting involved as a Speaker, please let us know. We would also welcome your input on companies, topics or specific persons you would like to see included on the agenda this year. We welcome your input into shaping the agenda sara.hook@pulseconferences.com.
Below are our 2026 past year Speakers.
/uploads/2024/11/Tom-Murphy.png)
Intelligence and Due Diligence Manager, Google DeepMind (UK)
Tom Murphy is Intelligence & Due Diligence Manager at Google DeepMind, which is Google’s AI division. His background is in intelligence, and he has extensive experience providing business-enabling security and political intelligence and analysis to some of the world’s most influential organisations.
At Google Deepmind, he has helped launch and/or run programs related to assessing Google DeepMind’s external risk environment, insider risk, due diligence, third party risk management, and vetting and back background checks.
Before Google DeepMind, Tom ran the Strategic Intelligence practice at global political risk intelligence firm Dragonfly, where he advised C-suite executives as well as corporate and information security leaders in blue chip clients across diverse sectors, including tech, financial services and critical infrastructure. Tom holds a MA in International Relations from the University of Melbourne.
/uploads/2025/08/James-Dorsey.jpg)
Adjunct Senior Fellow RSIS | S. Rajaratnam School of International Studies and Author (Singapore)
Dr. James M Dorsey is an award-winning journalist and scholar with four decades of experience covering many of the most momentous events in contemporary history, including multiple wars, insurgencies, and civil strife in the Middle East, Europe, Africa, Asia, and Latin America, the Iranian revolution, the demise of the Soviet Union and former Yugoslavia, the Israeli-Palestinian conflict, the politics of sports, and religious militancy. A former foreign correspondent for The Wall Street Journal, The New York Times, and the Financial Times, Dr. Dorsey was based in Washington, London, Paris, Athens, Istanbul, Jerusalem, Beirut, Tehran, Cairo, Dubai, Kuwait, Riyadh. Currently, he is an Adjunct Senior Fellow at the S. Rajaratnam School of International Studies in Singapore. As the author of the widely read newsletter The Turbulent World with James M Dorsey and books on the Middle East, Southeast Asia, and China, he is a widely recognized voice on international affairs, a frequent advisor to governments, corporations, and international institutions, and investigator for law firms and due diligence consultancies.
/uploads/2024/01/PK2.jpg)
Senior Director, Security, Atlas Air (US)
Patrick Kane is Senior Director Security for Atlas Air, a US airline conducting cargo and public/private passenger operations worldwide. Patrick is heavily focused on developing and implementing mitigation measures to support a highly mobile global workforce and multiple travelers, to include pre-travel risk assessments, coordinating secure transportation and journey management, assessing hotel and transportation options.
Patrick currently serves as the Chair of the ASIS International Santa Barbara Ventura Chapter #21 and is the President of the Corporate Executive Protection Leadership Council (CEPLC). He recently spearheaded the creation of a Travel Risk Working Group within ASIS International. Patrick is also the past Chair and Chair Emeritus of the OSAC Aviation Security Working Group. He has over 20 years of experience working in private sector corporate security; most of that time focused on international operations and has personal experience on the ground in more than 70 countries.
Since 1996 Patrick has been a Certified Protection Professional (CPP) in good standing under the auspices of ASIS International. He received an International Executive MBA from Instituto de Empresa in Madrid, Spain in 2004. Prior to entering the private sector, Patrick served as an infantry officer in the US Marine Corps. He welcomes questions, comments and suggestions and he can be reached at patrick.kane@atlasair.com or patrick.kane.cpp@gmail.com .
/uploads/2024/01/Meredith-Wilson.jpg)
CEO, Emergent Risk International (USA)
Meredith Wilson is the Founder and CEO of Emergent Risk International, LLC, which empowers companies to understand and address the impact of geopolitical events on their business. The company specializes in addressing risks and opportunities in emerging markets, political and security risk, and building strategic risk intelligence programs for multi-national companies and organizations. ERI provides consulting, training and advice to some of the largest multi-national companies in the US.
Ms. Wilson serves as a political risk and intelligence advisor to executive management and government and has more than 20 years experience in international environments, the energy sector, major corporations and the US intelligence community. Before founding Emergent Risk International, Ms. Wilson worked at the Pentagon for the US Defense Intelligence Agency. In 2007 she moved to the private sector to build a strategic intelligence program at ConocoPhillips. Subsequently she worked in regulatory affairs before moving on to Kosmos Energy to develop a political risk program. She served as a business intelligence advisor to the National Intelligence Officer for Science and Technology and provides briefings to executives and members of the USG and US military. She is a cofounder of the Private Sector Intelligence Council (PSIC), a member of the Board of Directors for the Association for International Risk and Intelligence Professionals (AIRIP), and an Advisory Board member for the Southeastern Analysts’ Roundtable. She has a Bachelor’s Degree in International Relations and a Masters Degree in History. Ms. Wilson has lived and worked in Australia, the UK, Ireland, Vietnam and Malaysia. She also has extensive experience working in the Middle East and Africa. She is available for speaking engagements related to geopolitical events and utilizing intelligence to build better business strategy.
/uploads/2020/01/Justin-Crump-1.jpg)
CEO and Founder of Sibylline (UK)
Justin is a military veteran with 25 years of full and part time experience. With degrees from the University of Durham and King’s College, London, he was initially a corporate finance analyst at JP Morgan Chase & Co before being called up for military service after 9/11. This started a security focused career that led to founding Sibylline. He continues to serve as a Challenger 2 Main Battle Tank commander with the Royal Wessex Yeomanry in the UK. His focus areas are global jihadism, the evolution of cyber and technical threats, and the creation of innovative and effective risk models. He is an acknowledged authority on business intelligence, global risk analysis and governance, the Vice President of the Association of International Risk Intelligence Professionals (AIRIP); a member of the UK Risk and Security Management Forum; on the steering group of the International Security Foundation; and mentors next generation military professionals starting in business through Heropreneurs. He has on-the-ground experience in over 65 countries and is a regular print and broadcast media commentator, as well as the author of Corporate Security Intelligence and Strategic Decision Making, the first work dedicated to the topic.
/uploads/2025/12/HH30123925_Chris_Meager.jpg)
Managing Partner, enteles Search (UK)
Chris Meager has spent twenty-two years working within the security profession, which has seen him work on CSO level searches for some of the largest multinationals in the world and place people in over 45 countries. Chris regularly speaks at industry events both in Europe and the US, on subjects ranging from Diversity & Inclusion, through to how a business’ culture can affect a CSO and the security management function. He has worked with companies to help them increase the diversity of their security and resilience functions, successfully targeting diverse candidates for roles ranging from CSO, to Regional Security Directors, and niche SMEs in intelligence and investigations. Chris holds a Post-Graduate Diploma in Security Management from Leicester University and is a member of ASIS International, the Security Institute and the Association of International Risk Intelligence Professionals. Chris also holds membership of APSCo, the leading industry body for the Executive Search profession and has the Certificate in Recruitment Practice from the Recruitment & Employment Confederation.
/uploads/2025/08/Eugene-Teo-both.jpg)
Chief Security Advisor ASEAN, Microsoft; Co-Chair, FAIR Institute Singapore Chapter; Member Finance Committee, Singapore Institute of Directors (SID)
Eugene Teo is Microsoft ASEAN’s Chief Security Advisor, partnering with enterprise CISOs to strengthen their cybersecurity programmes, strategy, and oversight. He also serves as the Data Protection Officer (DPO) for several Microsoft subsidiaries in ASEAN. Prior to Microsoft, Eugene was VP of Global Security at UKG (a PE-backed technology firm) and held leadership roles at Symantec and Red Hat. A dedicated industry leader, Eugene is the Co-Chair of the FAIR Institute (Singapore Chapter), a member of the Finance Committee at the Singapore Institute of Directors (SID), and a committee member at the Singapore Computer Society. His expertise is featured in the book “Tribe of Hackers Security Leaders,” and he is a frequent speaker at global security conferences. Eugene holds Bachelor’s and Master’s degrees in Computing from the National University of Singapore (NUS). He is an SID Accredited Board Director and a Boardroom Certified Qualified Technology Expert (QTE), holding CISM, CRISC, CIPM, and CIPP/E certifications.
/uploads/2025/12/IMG_7972.jpg)
Group Security Director, CRH Plc. (UK)
Gilad is an international security, risk, and resilience leader with over two decades of experience operating in complex and high‑risk environments. As International Security Director at CRH, he leads enterprise security risk management, crisis preparedness, and organisational resilience across Europe, Asia, and Australia, protecting large-scale manufacturing and global supply chain operations. Previously, Gilad held senior leadership roles at CEMEX, where he oversaw security and enterprise risk management across more than 700 operational sites, and at Control Risks, advising Fortune 500 organisations on risk appetite, security strategy, and crisis response worldwide. Gilad brings deep expertise in geopolitics, threat intelligence, insider risk, supply chain resilience, crisis leadership and business continuity management. He holds an MPhil in International Relations from the University of Cambridge and is a regular contributor to global security and resilience forums.
/uploads/2024/09/jason-lau.png)
CISO, Crypto.com
Jason Lau is currently the Chief Information Security Officer (CISO) at Crypto.com where he drives the global cybersecurity and information privacy strategy. Jason led his team to become the first cryptocurrency company in the world to have company-wide certifications in ISO 27001:2013, ISO 27701:2019, ISO 22301:2019, PCI:DSS 4.0, SOC2 Type 2 and meeting the highest “Adaptive” tier of the NIST Cybersecurity Framework and NIST Privacy Framework. Prior to this, Jason was a regional Cybersecurity Advisor at Microsoft, leading Microsoft’s cybersecurity initiatives in Asia Pacific. Jason holds the title of Adjunct Professor of cybersecurity and data privacy at one of Asia’s leading business schools, a member of the global ISACA Board of Directors, Advisory Board for BlackHat and former Asia Advisory Board, Co-Chair and faculty member of the International Association of Privacy Professionals (IAPP). Jason also sits on the advisory board of Tencent’s Finance Academy, advising on FinTech and cybersecurity ecosystem development in the region. Jason has over 24 years in consulting experience for Fortune 500 companies in the fields of management consulting, cybersecurity, IT governance, privacy and risk management, and holds certifications such as CISSP, CDPSE, CGEIT, CISA, CISM, CRISC, CIPP/E, CIPM, CIPT, CEH, CNDA, CSM, HCISPP and more. Jason has won multiple awards including the “Cybersecurity Professional Award”, and “Outstanding Financial Technologist of the Year (Data Privacy)”, and voted a “Top 50 global thought leader and influencer on cybersecurity”, selected by industry peers into the “Global CISO 100” and most recently, Business Magazine Executive of the Year for Cybersecurity and multiple CSO Online “CISO 30” winner. Jason also sits on industry advisory groups and participates on various global security and privacy think tanks like the World Economic Forum’s Expert Network, Centre for Information Policy Leadership (CIPL). Jason has over a decade in the Healthcare industry across 5 continents safeguarding highly sensitive Protected Health Information (PHI) for hospitals and healthcare providers, and is a certified HealthCare Information Security and Privacy Professional (HCISPP). Jason also sits on various industry committees on the cybersecurity risks and ethical use of Artificial Intelligence. Jason holds a bachelor degree in engineering (Honors) and bachelor degree in commerce, and completed executive programs at Stanford and Harvard
/uploads/2025/12/Mark-Wolsey-CSO.jpg)
CEO, Convergent Risk; Senior Security Advisor, International SOS. Former CSO for Smiths Group, Cadbury, Philip Morris International and CRH. Former Global Security Leader at PwC
As a graduate of Philosophy, Mark served 25 years as an officer in the Royal Marines, focusing mainly on counter terrorist operations and intelligence. He has spent the last 20 years in corporate security holding the most senior security leadership roles in several global organisations, serving as a trusted advisor to executive leadership and boards, and shaping enterprise-wide approaches to security, resilience, and crisis response. He has been the Chief Security Officer for Smiths Group, Cadbury, Philip Morris International and CRH and the Global Security Leader at PwC, where he led the client-facing Security Consultancy practice.
Throughout his military and commercial careers, Mark has been directly involved in most of the world’s significant crises, conflicts, and natural disasters, bringing deep expertise in crisis planning, response, and recovery. Most recently, he has been intimately involved in the Ukraine crisis, dividing his time equally between the UK and Ukraine, working closely with both nations’ military and intelligence organisations.
/uploads/2025/12/Martin-Petts-F24-CSO-and-CISO.jpg)
Head of APAC and Australasia, F24
Martin Petts has over 20 years’ experience in crisis management, emergency notification, IT business continuity, and data protection technology. He joined F24 more than eight years ago, where he has guided the digital transformation of critical communications and emergency and crisis management functions for over 30 organisations. Now leading F24’s efforts in the Asia Pacific and Oceania regions, Martin is dedicated to bringing his expertise to these underserved markets and collaborating with organisations seeking to use technology to advance their incident response and resilience capabilities through technology.
/uploads/2021/01/LEIVESLEY-Sally-34-Copy.jpg)
Director, Newrisk Ltd (UK)
Dr Sally Leivesley, Managing Director of Newrisk Limited in UK is interested in all catastrophic risks to people, infrastructure cyber security and to the stability of organisations and governments – see www. Newrisk.com, Sally@newrisk.com. Her current research focus is on the resilience of the First and Second Island Chains, escalating nuclear weapons risks and advances in bio-computing and brain science. She serves as an international media commentator for BBC World Service and other international news outlets including Australia on incidents such as the 2025 Heathrow Airport transformer fire outage, 2024 Paris Olympics rail sabotage, 2023 Chinese spy balloon over USA nuclear missile site; cyber threats; terrorism; aviation losses including MH370; nuclear reactor disasters; South China Sea; Polonium-210 and Novichok poisonings, Beslan siege; Iran; DPRK; and Covid-19.
In cyber and physical security she has worked closely with companies, governments and emergency services in the design and execution of large field exercises, table tops and board level exercises. She is currently designing and chairing a series of 10 international workshops on catastrophic risks including cyber and physical security, for Imperial College London. In London she served on a small panel of advisers for the first two UK government supported publications on ‘cyber security in the built environment’ published by the IET. Dr Leivesley is a Visiting Security Science Fellow for the Institute of Security and Technology, Imperial College London and holds memberships with the UK Register of Security Engineers and Specialists, the International Association of Bomb Technicians and Investigators, and the Royal United Services Institute for Defence Studies.
Dr Leivesley commenced her career in Australia working across banking cyber security, petrochemicals, oil and gas and mining infrastructure and worked on resilience of power generation and distribution, railways mainline and underground, bulk shipping, banking and other areas of critical industry as well as pioneering disaster unit leadership for major disasters. She is also a former British Scientific Advisor for all-out nuclear attack protection of the public, infrastructure and government and was trained by the British Home Office during the Cold War. She has been contracted during three nuclear power plant incidents to provide publications, reports and advice on public safety -–TMI, Chernobyl and Fukushima. In May 2024 she published with colleagues in the Bulletin of the Atomic Scientists the subject of formal risk assessments and nuclear arms control. She has spoken at many international events on energy security including the Electrical Infrastructure Security Council electric power industry meeting in the United States Capitol and to the USA Baker Institute on catastrophic supply chain risks.
/uploads/2025/12/CC.jpg)
Technical Leader, Office of the CTO, Cisco (Singapore)
Chris has over two decades of experience in information security, data privacy, and digital transformation; leading the business, design & delivery of innovative and effective solutions for complex and diverse challenges in various industries. As Technical Leader at Cisco, he collaborates with global customers, teams and partners to provide strategic guidance, technical advice, and thought leadership in Mobile Communications, Cloud, Enterprise Security Architectures, Managed Services, and Digital Trust. Chris is a Fellow of Information Privacy and a member of the Research Advisory Boards of the IAPP, where he contributes to the development and promotion of the profession, privacy engineering and domains of digital responsibility. He is also a member of the International Information System Security Certification Consortium (ISC2), a Member of the Open Worldwide Application Security Project® Foundation (OWASP), a Member of the Internet Society, a Corporate Member with Messaging Malware Mobile Anti-Abuse Working Group (M3AAWG), the Future of Privacy Forum (FPF), the Information Technology Industry Council (ITI), as well as being a Professional Member of the Singapore Computer Society (SCS). Chris is deeply passionate about advancing the professions of Digital Trust and information security to empower organizations and individuals to protect their data and assets in the information economy.
This years’ networking events are listed below. The 2027 events will be listed in due course closer to the event.
Sunday 10 May – 19:00-21:00
Inspired by the nearby Singapore Botanic Gardens, this lush, verdant space bathed in natural daylight, the breezy Garden@OneNinety is set in an alfresco terrace. Ideal for our informal and relaxed meet and greet!
/uploads/2026/05/128993759.jpg)
Monday 11 May – 18:00-21:00
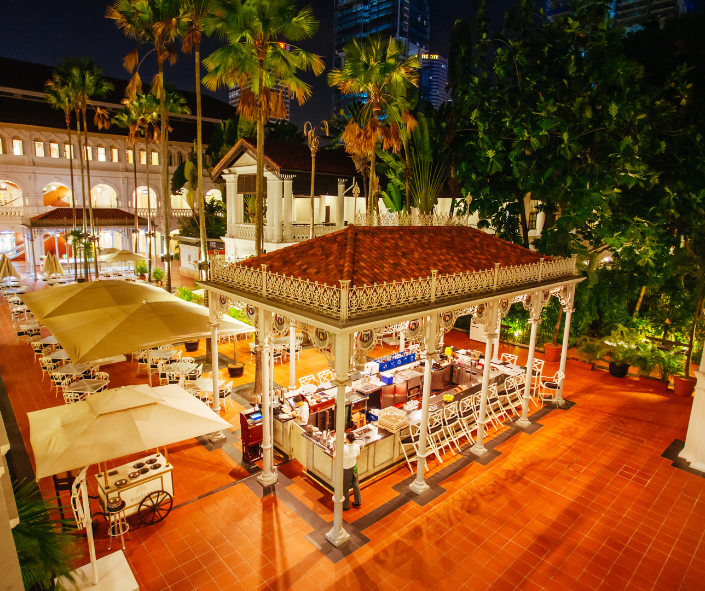
Tropically nestled amidst the swaying palms and white majestic arches, Raffles Courtyard exudes a welcoming vibe, inviting one into its lushly landscaped alfresco courtyard at the Raffles Arcade – perfect for the CISO + CSO 360 Supper! Slings and canapes.
/uploads/2026/05/Raffles-Hotel-Raffles-Courtyard.png)
/uploads/2024/01/1._High_Res_-_Chapter-logo-Rebrand-APAC_Region_Page_073-removebg-preview.png)
ISC2 Singapore Chapter is a non-profit membership community of ISC2 credential (information/ cyber-security professional certification) holders in Singapore, and other information /cyber-security practitioners.
We aim to advance the Singapore ecosystem of this domain by providing members with opportunities to network with industry peers, share knowledge (eg. advances in technology, techniques, current issues, trends and policies), exchange resources, collaborate on projects and business opportunities, and find new ways to advance development credits.
Our chapter and programs collaborate with Government Agencies, Industry leaders, IT-security and governance solutions providers, vendors and end-user customers, whom our members come from. The community also helps in development of leaders and professionals in the information systems security, as well as organize and participate in activities to promote awareness of the profession and also educate the public on personal cyber-security tips and best practices.
Chapter Mission
For more information, visit: www.isc2chapter.sg
/uploads/2025/12/WiCyS.jpg)
Women in CyberSecurity (WiCyS) Australia Affiliate is part of the global WiCyS community, a leading non-profit network focused on recruiting, retaining and advancing women in cybersecurity. WiCyS Australia exists to support women, non-binary and Indigenous Australians at every stage of their cybersecurity journey by creating opportunities for connection, visibility, mentoring, learning and leadership. Through partnerships across industry, academia, government and the wider community, WiCyS Australia helps strengthen a more diverse, inclusive and future-ready cyber workforce
For more information, visit: https://sites.google.com/wicys.org/wicysaustralia/home
About the Four Seasons Hotel Singapore.
Nestled along tree-lined Orchard Boulevard, Four Seasons Hotel Singapore is an oasis of calm in the heart of the city. 30 minutes from Changi International Airport, the Hotel is steps away from the shopping, entertainment and business belt of Orchard Road, and the picturesque Singapore Botanic Gardens, a UNESCO World Heritage Site. Featuring 259 guestrooms, the design aesthetics of the Hotel seamlessly blend contemporary luxury with rich cultural narratives, creating an immersive urban retreat. Expansive floor-to-ceiling windows in every guest room fill the space with natural light and provide sweeping views of the cityscape and lush greenery. With various dining and entertainment venues including Michelin-recommended Cantonese restaurant, Jiang-Nan Chun and celebrity chef Nobu Matsuhisa’s Nobu restaurant, the Hotel also offers 6,000 sqm. of health and wellness facilities which include two outdoor swimming pools, tennis, padel and pickleball courts, a 24-hour gym, premier medical clinic Chi Longevity and an award-winning Spa.
Car Park:
Pulse will provide complimentary parking at the Four Seasons Hotel. Upon arrival, please report to the Pulse registration desk in the Four Seasons Ballroom Foyer and scan the QR code provided. You will need to scan this code again at the exit machine when leaving the car park.
Pulse Conferences is pleased to offer an exclusive accommodation rate at the beautiful Four Seasons Hotel: SGD$390++/S$430++ per room per night (Single/Double)
Rate Per Night **Inclusive of Breakfast @ One-Ninety Restaurant and Complimentary Internet Access for unlimited device** (Single/Double).
The Group Code 260510PUN has been set up and the Hotel is ready to receive individual room reservation directly on the Four Seasons website. The system generates an instant confirmation.
Please email Reservations Team (res.fssingapore@fourseasons.com) for assistance or request for stay periods outside the nights of 10 and 11 May.
BOOKING INSTRUCTIONS:
BOOKING DEADLINE: Friday 24 April 2026
NOTES:
We are thrilled to have secured the stunning Four Seasons Ballroom to host the 1st CSO 360 and 5th CISO Asia & Oceania.
Four Seasons Hotel Singapore
A Luxury Sanctuary Along Singapore’s Orchard Road
190 Orchard Boulevard
/uploads/2025/08/level-3-pool.jpg)
/uploads/2025/08/519382350.jpg)
/uploads/2025/08/519382226.jpg)
/uploads/2025/08/420153455.jpg)
/uploads/2025/08/420145095.jpg)
/uploads/2025/08/128993759.jpg)
/uploads/2025/08/SIN_1804_original.jpg)
/uploads/2025/08/807908871.jpg)
/uploads/2025/08/420153414.jpg)
/uploads/2025/08/420139385.jpg)
Delegate Passes are available to book by in-house practitioners – i.e. persons who are doing a role as a Chief Security Officer and directors of corporate security, geopolitical risk intelligence, investigations, Risk, Resilience and other in-house executives roles.
RegisterWe have ring-fenced a limited number of Networking Passes, designed for senior executives working at provider, vendor or geopolitical risk and security advisories or as independent advisors to the security community. Through this type of networking participation, executives can benefit from the business development and learning opportunities of attending.
RegisterIf your participation has already been confirmed with the Pulse team, please use the below button to register.
Register* Pulse Conferences reserves the right to approve that registration is under the correct tier.
For purposes of these Terms “Attendee” shall mean all participant types at the event (Speakers, Sponsors, Delegates, Guests, Partners). By participating in this Event, you agree to these Terms.
Pulse Conferences events are intended for networking, collaboration and to provide inspiration amongst the security community. We generally assume that most people are intelligent and well-intended and we are not inclined to tell people what to do. Ensuring the positive and fulfilling experience of each participant in our community is our top priority. Accordingly:
Please bring any concerns during the event to the immediate attention of our team by emailing teampulse@pulseconferences.com
Pulse Conferences has the right to virtualise the programme, postpone the date or change the location of the event, if delay of performance is caused by circumstances or events outside of its reasonable control, which shall include but not be limited to industrial action, acts of God, terrorism, pandemic, power cuts or internet failure, civil commotion, refusals to grant licenses or permissions.
Attendees are encouraged to capture and their own event experiences in the permitted areas of the event venue, provided it does not defame other event attendees or infringe on copyrighted branding and content. Pulse Conferences leverages social media to post photos and videos to its social media feeds during the event.
By attending the Event, you acknowledge and agree that:
To read about Pulse Conferences Privacy Policy and download in pdf format please click below.
Download Pulse Conferences Privacy Policy here
Highlights Video from 2026 will be posted soon
F24 - Resilience: Vision 2030 Report
F24 - Emergency & Crisis Communications Report 2025
Emergency & Crisis Communications Report 2025
F24 - Incident Management: Stop an Incident from Becoming a Crisis
F24 - Communication During a Crisis: How to Make Your Communication Infrastructure Crisis-Proof
International SOS - Build an Appropriate and Effective Crisis Management Program
International SOS - Natural Hazards: How to Prepare for the Unpredictable“Being the first Pulse Conference I attended, it was an absolute masterclass. The program, the speakers, the ambience – everything was well thought of. Excellent”
Azhary Saleh, ASCC Manager, The Walt Disney Company (Singapore)“I felt it was a great session for networking and some of the presentations were helpful in identifying some emerging trends that we might experience in security”
“If you want to hear real CISO experiences, you must attend this event!”
Chuan-Wei Hoo, CISO, ST Engineering, Singapore
“Amazing speakers, very engaging and educational, professional, and extremely well organized. Looking forward to the next events.”
Allen Alexandra Mercz, Cybersecurity and Data Privacy Director (Singapore)
“Amazing speakers, very engaging and educational, professional, and extremely well organized. Looking forward to the next events.”
Allen Ohanian Chief Information Security Officer LA County DCFS
“A lot of golden nuggets have been discussed during the conference. Its a great community with excellent people!!”
Denis Ponomarev, Principal Cybersecurity Officer APAC and China, Siemens Energy
“Fantastic – Champions League Cyber Event”
Steve Ramsden, CISO, Head of Innovation, The Global Fund (Switzerland)
“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!”
Manoj Wadhowa, Senior Manager, Cybersecurity, EY Singapore
“A very thoughtful event, great networking and industrial expertise in the room to learn from!”
Ryan Chan, Director, Security, Laureate International Universities Malaysia
“Just wanted to say thanks to you and the team for a really well-organised event – I definitely benefited from the speaker’s sharing and the networking.”
Regional Security Crisis Manager, Bio-pharmaceutical Company, Singapore
“It seemed like everything was perfectly set to ensure a smooth event gathering 100+ valued guests. Loved the energy, the talks, the stands and also the choice of networking activities!”
CISO, Engie (France)
“CISO 360 Global Congress is **the** congress for CISOs and senior cybersecurity practitioners to attend. The scope of topics presented is excellent!”
CISO, DPO and Director of the Internal Control Office, Comissao do Mercado de Valores Mobilia¡rios, Portugal
“CISO 360 is the perfect balance between working, socialising, and networking. So the appealing thing about coming here is you get to meet a load of people that you wouldn’t normally get in front of, so there’s some smaller vendors who if you Google certain area they’re probably not going to come up in the first page and you get to meet them and they get to tell you about their interesting new take on the technology, and you get to do it in a really nice setting, it’s a lovely hotel, the events that Pulse put on outside of the hotel are really good, where you get to socialise with people and after a couple of drinks they kind of tell you a bit more truthfully what their products can do which is really, really useful. And then you get to do the follow-on, the boring stuff where they take you through a slide deck in London afterwards, so you get to meet them properly first, and then learn about the bumph that they’ve got from their sales team afterwards so that’s really cool.”
Security Operations Manager, Right Move
“The CISO 360 Congress provided a unique platform to explore the delicate balance between innovation and practical implementation in cybersecurity. As a startup founder, I found the discussions on DevSecOps challenges and the evolving role of CISOs particularly enlightening. One key takeaway was the constant tension between designing for scale and the risk of over-engineering. In the startup world, we must be agile, forward-thinking, and grounded in current market needs. The debates around Generative AI highlighted this balance perfectly. These events are crucial for widening our horizons and engaging in insightful discussions with peers. They remind us that while pushing the boundaries of technology, we must always keep sight of the practical challenges security leaders face in their day-to-day operations. This blend of innovation and practicality will drive our industry forward.”
CTO and Co-Founder, JIT (Israel)
“As a newcomer to the cybersecurity event scene, CISO 360 was an eye-opener. I expected a highly technical environment but instead found a deeply human-centric experience. It revealed the true challenges and struggles that CISOs face daily. This insight is invaluable for someone in my role, as it helps bridge the gap between our products and the real-world needs of security leaders. The event’s structure, starting with a candid roundtable discussion, set the tone for the entire conference. It allowed us to view subsequent presentations and discussions through the lens of solving real problems.”
Regional Executive, KnowBe4 (The Netherlands)
“Great conference! From the beginning, the level of participant engagement was very high. The content was very informative and the presenters very knowledgeable. Every aspect of Global CISO 360 was extraordinarily well done. I left the event with a better understanding of cybersecurity and a broader network of industry contacts.”
Senior Director Security, Atlas Air (United States)
“Extremely insightful talks and a great way to connect with others in the industry that fostered genuine and open discussions”
Cyber and Geopolitical Risk lead, Sibylline (UK)
“Superb line-up of speakers and topics! The sequence of the ’roundtable’ at beginning, prior to ‘sitting down’ at the conference, was a very good ‘icebreaker’, socially, and this allowed us to get to know one another well. Content and organization made this an excellent event!”
CISO, Infopercept (UK)
“A great experience – I liked the fact that the Pulse team had the energy to support and make this such an experience – everyone was friendly and there to support when needed”
Senior Account Executive, Hack the Box (Greece)
“One of the biggest challenges in our industry is gaining access to open conversations with CISOs without prior introductions. Cold calling and traditional outreach methods often fall short. However, events like CISO 360 create an environment where everyone is approachable, solving this challenge elegantly. The casual atmosphere fosters open dialogue, allowing us to understand CISOs’ current challenges and how we can help. It’s not just about selling; it’s about building meaningful connections. These events provide a unique opportunity to engage in positive conversations and establish good relationships that lead to fruitful collaborations.”
GemServ, a Talan Group company (UK)
“As vendors, we’re often seen as just another salesperson despite our genuine desire to help improve the industry. Events like CISO 360 are invaluable for fostering connections. They open doors to future introductions, lunches, and even inclusion in specialised groups. These connections are the foundation of true industry collaboration. Interestingly, the most effective collaboration often happens off the record – in WhatsApp groups, over coffee, or during casual lunches. These spaces allow security professionals to share challenges without fear of oversharing or repercussions. To truly advance our industry, we need to encourage more of these human-to-human interactions.”
COO, Risk Ledger (UK)
“What I like about this CISO 360 conference is the peer interaction, the themes that we discuss here that are very relevant, the chance to speak openly in a way that you know that people will understand your problems and give you ideas. You can give something back and contribute to what could be the global outcome of the conference. It’s a sum of all the contributions, both people that do the presentations, the questions, the comments that we make. These things are all relevant, the speakers are well chosen, they are respected professionals on their fields, and the organisation is top, and the venue is always very beautiful place, everything is well organised so it’s highly recommended. Every time I attend CISO 360, I meet new people, there are faces that I see from year to year, some well-known. You see people from Asia, from America, from Europe, it’s mainly a European event but you see people coming from other continents, and it’s a very friendly modern atmosphere where people are at ease, everyone respects each other and we know that we can trust these people, we can share our problems, the questions we have, and there’s someone that went through the same thing and can give us an idea of what to do. I’m leaving with lots of new ideas for things that I want to implement and experiment, so that’s why I came, and that’s why people should come to these conferences, it’s great.”
Director of the Internal Control Office, Comissão do Mercado de Valores Mobiliários
“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”
CTO, Quod Orbis
“One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive).”
CISO & DPO, 360 Treasury Systems AG, Germany
“A very thoughtful event, great networking and industrial expertise in the room to learn from!”
Director, Security, Laureate International Universities Malaysia
“A meticulous and engaging event highlighting the key security concerns business leaders face today!”
Director, Bestman Solutions
“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.”
CMO, SailPoint
“Insights and experience shared by industry leaders will definitely help me and my organisation in course correcting the strategy”
Senior Cybersecurity, Lafarge Holcim
“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.”
CEO, Cordery
“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.” –
CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal
“Once you attend CISO 360, you become a part of the family. The socialising offered is the most important aspect. This community building through shared experiences makes it different from other conferences!”
CISO, Head of Information Security and Assurance Services ILO – United Nations, Switzerland
“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.”
Global Deputy CISO, Cushman & Wakefield
“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”
Chief Scientist and SVP of AI, Dataminr
“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to Sara, Clive and the team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good. Afterwards the meal sponsored by Qualys was fantastic. These are the smallest things that Pulse do for individuals such as myself that they don’t need to do, but they go out of their way just to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”
VP Information Security EMEA, Northern Trust
“It’s probably one of the best conferences for cybersecurity professionals. We really get to exchange information with other professors and peers in this industry, we build trust among us in this inclusive environment. We can exchange not only challenges, but celebrate the successes as well. And I would come back any time. We build not only trust and become friends, but also become part of the family. For CISOs it’s one of the most important things. Everybody expects CISOs to be very technical, and we are, but I believe that being very good on the soft skills is vital as well, and building that network is one of the most important things because CISOs cannot work alone. It’s almost impossible that you will know every single answer, so the networking is probably the most important thing in our field to pick up the phone, to say: “Hey, are you having the same challenge, how are you doing things around these problems or issues?” It really does help, and it’s proven itself over and over again. I use the CISO 360 network and call people. Besides information sharing, besides the fact that we all have become friends and family here, I would say we also have great evening events, which is how we build a stronger connection. CISO 360 is the place to be. I recommend it to all of our professionals in cybersecurity.”
CISO European Investment Bank
“This is a very good event for meeting CISOs, security professionals, and the vendors to learn more about what is going on, their challenges, and how to deal with them. This event has a number of really amazing speakers. Some of them have been in this industry for a long, long, long time, they have a broad variety of experiences, they share these experiences and they are still today trying to learn the next thing. There are three big benefits to attending CISO 360. The networking is one. You need to be able to share what you know and learn from others. The content from the stage is a second one, obviously, and the third one is the social aspect. We have a boat trip and wine tasting. Work is fine, but you also need to be personal, you need to bring those connections in because you never know when you need to pick up that phone and say: “Hey, I have this issue, I don’t know who to discuss it with, but I trust you.”
CEO and Founder, Praxis Security
“Thank you for the excellent event and seamless organisation! It was my first time at the CISO 360 and the event was highly inspiring with great networking opportunities.”
Senior Consultant, DHC AG (Switzerland)
“We’ve been with Pulse and the CISO 360 since it started, and it’s been an amazing journey and we’ve created this community and this family, we see new faces, the same faces. And one of the issues we have in our industry is the lack of communication, the lack of talking, so these events are bringing people, bringing our peers out to have those talks, it’s great for vendors, it’s great for the community. If another vendor is thinking about joining this community do it. There is a fantastic community. We get to talk between the vendors as well, meet new people, see old friends, and how they are progressing through the industry as well – they may have moved, gone to new roles, new jobs, new organisations, and it’s great to see them transitioning. So we learn an awful lot as well as the customers do from learning from what we have as a vendor. We talk about diversity an awful lot in this industry and I think Pulse has managed to grab that with its agenda and its itinerary, there is something for everybody throughout the two days, through the day and through the evening as well and I think that’s one of the reasons why it captures such a wide range of audience, it’s because we are talking about so many different topics that are burning, these are topics that customers and vendors are having internally, so Pulse is giving you the opportunity to bring them out and allow people to talk about them.”
CTO UK, Qualys
“It’s a really cool event, a lot of CISOs come to these events and it’s quite a small little community where they all do a lot of learning and a lot of conversations. As a start-up, CISO 360 is a great way to meet people and build relationships within the industry. As a start-up, we don’t have the marketing budgets of big companies, so for us relationships are really important, we need to build trust with the CISOs, they need to trust us before using our products, and that was a really great way to come to an event like this, meet CISOs, teach them a bit about what we’re doing and what we’re trying to achieve with our mission and then from there hopefully get a few using the product. Gather feedback on our products has been really good for two reasons, firstly we’ve got a lot of constructive feedback on what we’re doing, what we’re trying to achieve, and actually new ways which we can achieve that, and secondly we’ve got a lot of people who are willing to try the product and actually join the trial and get using it. It’s a very well organised event with really friendly people. It’s always a great venue as well – they rotate it around different cities and it’s always nice to come to a different part of the world and meet people in a setting that’s not London.”
CEO, Risk Ledger
“I keep coming back to CISO 360, because I learn so much. There is such a breadth of information, people from right across all sorts of industries, and organisational titles. The breadth of the agenda is just amazing, and it’s really fascinating, and so I keep coming back because I want more. I’ve learned so much in the last couple of days about all sorts of different topics, from the really scary from Dr. Sally Leivesley’s presentation to areas about recruiting people, and what makes up a good team, and data governance. There is such a plethora of information, it’s impossible to do without CISO 360, so I come back for more – and I’ll be back next year. I think the atmosphere in this group is really open, it’s very friendly, they’re very welcoming. We like people, we talk to people, and nobody was left alone at the networking events. It’s a very inclusive group, and we welcome new people coming along because we want new experiences, we want to talk to new people. The really good thing about this group is that you can come along and have a really easy conversation about information security, cybersecurity, anything to do with security because this is a really knowledgeable audience, and it makes it easy and it’s very relaxed, you don’t have to fight anybody, everybody understands. It’s simply great.”
Head of Information Security, Quilter
“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.”
Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, United Kingdom
“What a week! Such a lovely venue, lovely city, and a fantastic collective of like-minded professionals. This was my first Annual CISO Congress, but not my first Pulse event, and Pulse did not fail to deliver their exceptional services once again. Sara and the team did a wonderful job, and pulled everything off brilliantly.”
Threat and Vulnerability Consultant, Computacenter, United Kingdom
“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way. The Pulse Conferences team puts this together from the heart.”
CISO, HARIBO (Germany)
“Where else can you find a higher quality of security leaders all in one place?”
Director, Bestman Solutions
“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.”
Information Security Compliance and Assurance Director, Flight Centre UK
“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”
Europe Industries- Security Officer, Air Liquide GMS (France)
“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.”
Director, Resilient World
“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.”
Technology Services Head of Cyber Security, DWP (UK)
“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the CISO 360 Congress. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.”
Peter Wood, Naturally Cyber LLP
“Excellent conference”
Barbara Aung, CISO, Telefonica
“This was great, we have a lot of good take away’s and loved the lessons learned!”
Sybil Kleinmichel, 360 Treasury Systems AG
“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting”
CMO, Vectra
“If you want to hear real CISO experiences, you must attend this event!”
CISO, ST Engineering, Singapore
“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC
“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.”
CMO, NetClean
“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!”
Senior Manager, Cybersecurity, EY Singapore
“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!”
Chief Privacy Officer, Nokia Group
“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.”
CMO, SailPoint
“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!”
Group CISO and Group DPO, MS Amlin
“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.”
CMO, Synack
“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.”
CMO, Telstra
“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ”
Supporting Organisation, ClubCISO
“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”,
President, (ISC)2 Scotland Chapter
“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape”
GRC Specialist, Euronext
“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!”
CISO, GOPA International Energy (Abu Dhabi)
“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin
“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”,
Director Security Engineering, Inmarsat
“A very engaging, varied and interactive event. The best conference I have ever attended!”
Information Security Manager, Lloyd’s of London
“The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government
“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”
CISO, Channel 4
“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ”
Director Sales, Sailpoint
“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA
CISO 360 Congress created a strong platform for peer review, cross pollination of idea and networking.”
CISO, Gebauer & Griller
“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”
CSO, Logista Portugal
“Pulse Conferences stand out for being up to the minute with developments and concerns. First rate speakers and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum
“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Cygenta (USA)
“Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Cygenta (USA)
“Excellent conference, brilliantly put together.”
Director, Bridewell
“Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall
“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!”
Director of Information Security EMEA, Canon Europe (UK)
“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!”
Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!”
Corporate Security Manager, Logista (Portugal)
“Marvellous event, well-run, packed with useful content you can use”,
Technology Services Head of Security, DWP
“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland
“I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV (Spain)
“Refreshing views of security topics for knowledge improvement!”
CISO, Bank Credibom (Portugal)
“Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv
Telephone: +44 (0)20 3455 9444
Email: teampulse@pulseconferences.com
Sponsorship: sponsorship@pulseconferences.com
Pulse Conferences on LinkedIn