https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-madrid-01.jpg

https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-madrid-02.jpg

https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-madrid-03.jpg

https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-madrid-04.jpg

https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-madrid-05.jpg

https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-madrid-06.jpg

https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-madrid-07.jpg

https://pulseconferences-3802924.hs-sites.com/hubfs/3802924/Event%20Sliders/pulse-slider-madrid-08.jpg

CISO 360 Global Congress

11th CISO 360 Global Congress

Securing the Age of AI: Innovation with Resilience

Three days of peer-to-peer exchange for CISOs and senior security leaders from around the world.

  • Dates23–25 June 2027
  • VenueMadrid, Spain

Eleven Years of CISO 360 Peer to Peer.

Welcome to the 11th CISO 360 Global Congress

Securing the Age of AI: Innovation with Resilience
Share. Compare. Be Inspired by Peers

📅23-25 June 2027📍Europe | City to be announced

Register for 2027Find out more about sponsoring this event2026 Event Materials

Following our milestone 10th anniversary edition in Lisbon, the CISO 360 Global Congress returns in June 2027 — bringing visionaries, leaders and innovators together to talk security.

Practitioner-Led | Real-World | Peer-to-Peer

Created and hosted by Pulse, the 11th Flagship CISO 360 Global Congress will bring together CISOs and international cybersecurity leaders from across the globe. Building on a decade of trusted dialogue — most recently our 10th anniversary edition at the Palácio Estoril, Lisbon — the 2027 congress opens the second decade of CISO 360.

CISOs from across the globe will share their strategies, explore emerging trends, and benchmark the latest tactics and tools to confront the rapidly evolving cybersecurity landscape. We will challenge the status quo through case stories, journeys, fireside chats, table think tanks, and the ever-popular CISO 360 Roundtable that kick-starts the event (half-day afternoon on 23 June).

Evening networking events, cultural excursions and exclusive dinners will create the backdrop for building lasting professional relationships and strengthening the global cybersecurity community.

The 2027 International Speaker Panel will feature CISOs, subject matter experts and senior leaders, with keynotes from leading voices in cybersecurity. Expect insights on AI, quantum computing, IoT/OT security, cyber geopolitics, cloud, human security and much more.

Highlights from Lisbon 2026

Key Themes for 2027 will be researched and firmed up organically.
2026 topics included:

  • AI and Quantum: Preparing for the next frontiers
  • Collaboration and innovation: Building alliances to tackle global cyber threats
  • Resilience and threat intelligence: Strengthening detection, response and recovery plans against a volatile threat landscape
  • CISO GRC toolkits and updates
  • CISO 360 Playbooks by key verticals
  • Cyber geopolitics and supply chain security: Navigating risk in a connected world

Why Join

Connect with peers facing similar risks and opportunities. A chance to:

  • Build trusted contacts — collaborate with CISOs, senior practitioners and global business leaders in a trusted environment, under The Chatham House Rule.
  • Stay future-focused — gain insights from risk managers and technology experts across sectors, helping you stay ahead of the curve.
  • Engage in collaborative projects — take part in meaningful conversations and projects with innovators, investors and thought leaders from around the world.

Join us in June 2027 as CISO 360 begins its second decade of cybersecurity leadership!

The 2026 International Speaker Panel will feature CISOs, subject matter experts, and visionary leaders, including keynotes from some of the world’s foremost voices in cybersecurity. You’ll hear cutting-edge insights on AI, quantum computing, IoT/OT security, cyber geopolitics, cloud, human security, and much more.

Connect with peers facing similar risks and opportunities. A perfect time to:

  • Build Trusted Contacts – Collaborate with CISOs, senior practitioners, and global business leaders in a trusted environment.
  • Stay future-focused – Gain insights from risk managers and technology experts across sectors, helping you stay ahead of the curve.
  • Engage in collaborative projects – Participate in meaningful dialogues and projects with innovators, investors, and thought leaders from around the world.

Join us in Lisbon for our 10th anniversary celebration. A decade of cybersecurity leadership converges with the future of digital resilience!

2026 Speakers included

Nuno Teodoro
Global Cybersecurity Director
Hovione
Portugal

Gemma Ungoed-Thomas
Senior Fellow, King’s College London
Former Director for State Threats, Cyber and Technology, UK Cabinet Office
UK

Giulia Moschini
CISO
Leroy Merlin Italy
Italy

Toks Oladuti
Global CISO
Dentons
UK

Alyssa Miller
CISO
Epiq Global
USA 

Munawar Valiji
Group CISO
Close Brothers
UK

Jorge Pinto
Information Security Specialist
Siemens
Portugal

Andrea Litherland
CISO
Domestic and General
UK

Stefan Weber
COO Digital Platform (Vertriebsplattform)
Deutsche Bahn Fernverkehr AG
Germany

Jelena Matone
CISO
European Investment Bank
Luxembourg

Dennis Pokupec
CSO/CISO
Creditplus Bank AG
Germany

Adam Drabik
CISO
SKF
UK

Jorge Fernandes       
CISO   
Comissao do Mercado de Valores Mobiliarios
Portugal
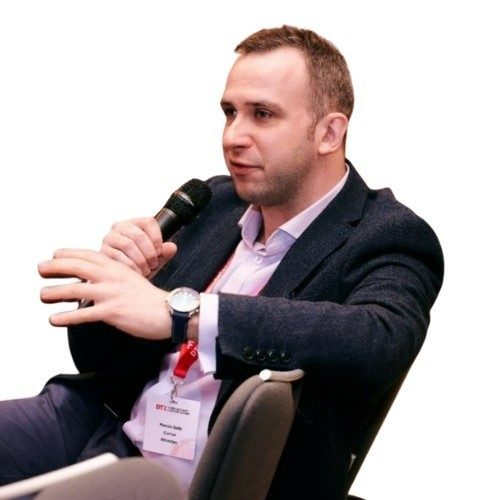
Marcin Roth
Senior Cyber Security Manager
Currys Plc
UK

Irene Corpuz
Co-Founder and Board Member
Women in Cyber Security Middle East
UAE

“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to the Pulse team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good. Afterwards the meal sponsored by Qualys was fantastic. These are the smallest things that Pulse do for individuals such as myself that they don’t need to do, but they go out of their way just to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”
Ibraheem Khan, VP Information Security EMEA, at a financial services firm

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”
Dr. Alex Jaimes, Chief Scientist and SVP of AI, Dataminr

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”
Gary Penolver, CTO, Quod Orbis

Welcome and many thanks to our CISO 360 Global Congress 2027 Sponsors (partial list)

Platinum Protectors

Pulse Conference Sponsor

CISO 360 Innovators

Pulse Conference Sponsor

With thanks to our sponsors

Platinum Protector & Networking Sponsor

Dataminr

CISO 360 Innovator

Intel 471

Platinum Protectors & Networking

Mastercard CybersecurityBridewellQualysDataminr

Platinum Protectors

KovrrTorq

Emerald Enforcer

CSC

Innovator Sponsors

ValidatoIntel 471AnecdotesThreatLocker

Supporting Organisations

AP2SIInformation Security Forum

Many thanks to our enabling Anchor Partners: Mastercard, Dataminr, Sibylline, Restrata, Reliance Cyber, Qualys, Emergent Risk International, ThreatLocker, Intel 471

The 2027 agenda is in research.

Agenda 2026

Speakers – 11th CISO 360 Global Congress 2027

The 2027 programme is currently being developed. If you would be interested in getting involved as a Speaker, please let us know. We would also welcome your input on companies, topics or specific persons you would like to see included on the agenda this year. We welcome your input into shaping the agenda sara.hook@pulseconferences.com.

The 2026 Speaker Panel included

Gemma Ungoed-Thomas, Senior Fellow, King’s College London. Recent Director for State Threats, Cyber and Technology in the UK Cabinet Office


Gemma Ungoed-Thomas is a Senior Fellow at King’s College London, working on issues at the intersection of national security, cyber power, emerging technology and democratic resilience. She brings extensive experience from senior roles in the UK government, where she led national strategy on state threats, cyber security and technology policy. Until March 2026, Gemma served as Director for State Threats, Cyber and Technology in the UK Cabinet Office. In this role she led national strategy at the intersection of security, advanced technology and resilience. She helped shape the UK’s £2 billion National Cyber Strategy, developed the UK’s first Counter State Threats Strategy, and co-chaired the National Cyber Advisory Board, bringing together senior leaders across government, industry and civil society to strengthen systemic resilience. She also served as Principal Adviser to the Prime Minister–chaired Science and Technology Committee. During her time in government, Gemma coordinated aspects of the UK’s support to Ukraine following the Russian invasion and led work to manage the UK’s risk exposure to hostile state activity, including malicious cyber and physical attacks.  Gemma has extensive experience in strategy, crisis management and national security decision-making. She previously served as Private Secretary to the Prime Minister for Home Affairs and National Security, leading cross-government responses to counter-terrorism incidents, national cyber attacks and major crises, including the Afghanistan evacuation. At the National Cyber Security Centre (NCSC), Gemma established and led national incident response teams and helped build the UK’s cyber incident response capability, overseeing multidisciplinary operations responding to the most significant national cyberattacks. She coordinated real-time operational response and strategic decision-making for ministers, industry leaders and critical infrastructure. Earlier in her career she held senior roles at GCHQ, leading cross-government cyber defence initiatives and contributing to the development of the UK’s first National Offensive Cyber Strategy. Her work focuses on resilience as a strategic pillar of national power, integrating behavioural insight, adaptive governance and international cooperation. She has advanced resilience frameworks with Five Eyes partners, the EU and the United States, and contributes to debates on democratic resilience, responsible AI governance and the security implications of emerging technologies.

2026 International Speaker Panel Lisbon 2026 (partial list)

Andrea Litherland

Andrea Litherland

CISO, Domestic and General (UK)

Alyssa Miller

Alyssa Miller

CISO, Epiq Global (USA)

Alyssa Miller is the Chief Information Security Officer for Epiq Global, responsible for evolving the global cybersecurity program. A childhood hacker turned cybersecurity executive, Alyssa combines a unique blend of technical expertise and leadership pedigree to drive innovation in securing people, processes, and technology. Alyssa’s career spans two and a half decades with some of the most recognizable names in financial services and consulting including FIS, Ernst & Young, and S&P Global. She has a track record of building and growing comprehensive security programs that address the ever-evolving threat landscape in today’s interconnected digital world. Alyssa is also internationally recognized within the cybersecurity community. She presents regularly at some of the top cybersecurity and industry events around the globe. Additionally, she’s a published author and a respected advocate within the cybersecurity community. Alyssa drives focus on reshaping the interconnection of cybersecurity practices with the enablement of business innovation and acceleration. 

Adam Drabik

Adam Drabik

CISO, SKF (UK)

Adam has 25 years international experience in managing IT and Information Security mainly in Oil & Gas, Pharmaceutical, Consumer Goods, Telecommunication and Financial Services industries. Founding member of ClubCISO, Consumer Goods Security Forum in the UK and Information Security Forum in Malaysia – peer groups of CISOs and Heads of Information Security formed to exchange good practices and experience within specific focus groups. Adam has significant experience consulting and advising boards of directors of FTSE100/Fortune500 companies on Information Security, Privacy, Risk Management and Resilience. The current role is Chief Information Security Officer at SKF. 

Alan Jenkins

Alan Jenkins

Principal Consultant, The Cyber Navigators (UK)

Alan was formerly Group CISO at Babcock International, UK CSO at CSC and T-Systems, an Associate Partner at IBM Security, and served in the Royal Air Force for 21 years.

https://www.linkedin.com/in/alanjenkins/

Archie Millett

Archie Millett

MA in the King's College London War Studies Department and Lead Analyst on Russian Hybrid Warfare, Defence and Security Forum (UK)

Archie Millett is a cybersecurity and security studies specialist currently completing an MA in the King’s College London War Studies Department. He serves as Lead Analyst on Russian Hybrid Warfare at the Defence and Security Forum, where he examines the intersection of cyber operations and geopolitical strategy. His research places particular emphasis on Russia’s use of cyber capabilities as part of its broader hybrid warfare approach.

Archie has been involved in multiple projects, including a new initiative titled The Resilience Imperative, which explores national preparedness in the UK and Europe in response to the growing threat posed by Russian cyber activity.

Archie is an engaging public speaker who brings together academic insight and real-world analysis to unpack cyber threats.

Brian Brackenborough

Brian Brackenborough

CISO

A cybersecurity leader with over 20 years’ experience helping to protect some of the UK’s most iconic broadcasters, Brian’s work has centred on strengthening resilience, improving security maturity, and enabling fast, creative media environments to operate safely in a complex and rapidly evolving threat landscape. Over the years he has delivered major transformation programmes, uplifted ISO 27001 and NIST maturity, and led Channel 4’s approach to CAF and the Cyber Resilience Act. He is passionate about making cybersecurity clear, practical and genuinely useful to the people who rely on it, from technology teams to senior leadership. He also contributed to sector-wide resilience by chairing cross-industry security groups and working closely with government bodies and NCSC. Brian enjoys turning complex challenges into straightforward insight and supporting teams in making confident, well-informed decisions. His focus is simple: build strong teams, drive meaningful improvement, and help organisations (large or small) raise their cyber resilience in a way that supports how they actually work.

Barry Coatesworth

Barry Coatesworth

Cyber Security Advisor, UK Government (UK)

Barry Coatesworth is one of the UK’s most accomplished cyber security leaders, with over three decades of experience protecting critical institutions across financial services, fintech, insurance, critical national infrastructure, and the public sector. Trusted by boards, regulators, and executive teams, he has served as Group CISO and board Advisor, and currently holds a senior advisory role securing critical UK Government financial infrastructure. Barry chairs a national cyber security authority and is one of the most influential voices shaping cyber security standards across the UK pensions and financial sector. Trusted by regulators and government alike, he has guided organisations through risk, transformation, and crisis with authority and confidence. An established author and international speaker, his published work includes The Psychology of Social Engineering in Cyber Security: A Peer-Reviewed Journal.”

Chris Gunner

Chris Gunner

vCISO, Thrive (UK)

Daniel Norman

Daniel Norman

Regional Director, EMEA, Information Security Forum (ISF)

Daniel is responsible for providing information security advisory services and best practices to over 250 Forbes/Fortune-sized companies across EMEA. Dan is a published author with specialisms in cyber simulation exercises, resilience, crisis preparedness, threat forecasting and behavuiour change. He has been a regular contributor to international magazines and conferences, including Dark Reading, SECURITY Middle East, InfoSecurity Europe and Computer Weekly, covering a range of security and risk management topics.

Dennis Pokupec

Dennis Pokupec

CSO/CISO, Creditplus Bank AG (Germany)

With over a decade of experience in Information Security and Risk Management, Dennis Pokupec has established himself as a leader in cybersecurity, blending technical expertise with strategic vision.
Education and Early Career: After earning a degree in Security and Safety Engineering, Dennis began his career as a Consultant at Sopra Steria Consulting (2015–2019). His dedication and skills quickly paved the way to leadership roles.
Professional Achievements: From 2019 to 2022, Dennis served as Chief Information Security Officer (CISO) at Viridium Group, where he developed and implemented robust cybersecurity frameworks. In 2022, he advanced to Chief Security Officer (CSO) at Creditplus Bank AG, a position he continues to hold, overseeing enterprise-wide security initiatives. In 2024, Dennis expanded his professional scope by offering freelance consulting in cybersecurity and risk management and CISO COaching, in addition to his role at Creditplus Bank AG. That same year, he also became a public speaker, sharing his insights and experiences on national and international stages. His contributions to the field were recognized with the prestigious CIO200 Next-Gen Award (2024).

Dr. Eduardo Solana

Dr. Eduardo Solana

Senior Lecturer of Cryptography and Security, University of Geneva (Switzerland)

Dr. Eduardo Solana is head of the Cryptography and Security group at the University of Geneva. Amongst others, he has worked for IBM and PricewaterhouseCoopers where he was Global Subject Matter Expert for authentication solutions. He has more than 30 years of experience in the fields of cryptography and information security both in the private sector land the academia. Dr. Solana is a deeply experienced security practitioner, technical writer and regular speaker at the most relevant conferences and symposia in the field. During his extensive career, he has provided consulting services to multinational organizations and states in cryptography and cybersecurity related issues

Eric Martínez Cancela

Eric Martínez Cancela

CISO for Spain and Portugal, Serunion, part of the Elior Group (Spain)

Eric Martínez Cancela is the Chief Information Security Officer (CISO) for Spain and Portugal at Serunion, part of the Elior Group, where he leads the cybersecurity strategy, governance, risk management, compliance, and security operations across the Iberian region.

At Serunion, Eric is currently leading key strategic cybersecurity programmes, including ISO 27001 alignment, ENS certification initiatives, NIS2 readiness, identity and access management improvements, security awareness programmes, vulnerability management, and the protection of business-critical services across a large and geographically distributed organisation.

His passion lies in bridging the gap between technical cybersecurity operations and executive decision-making, helping organisations transform cybersecurity into a business enabler and strategic function.

Giulia Moschini

Giulia Moschini

CISO, Leroy Merlin Italy (Italy)

Giulia is a CISO for Leroy Merlin Italy, the Italian branch of Adeo Group, Europe’s largest DIY retailer. She has built a security function while navigating regulatory complexity, large-scale technology projects, and organizational change. Her work focuses on cyber resilience, risk governance, digital product security and security culture, with a particular interest in the social impact of cybersecurity and in building adaptive, trust-based security models that connect technology, business and people. 

Indy Dhiman

Indy Dhiman

Information Security Officer, Humana (USA)

Indy Dhiman is a cybersecurity powerhouse with 15+ years of experience leading enterprise security strategy, cyber resilience, and digital transformation initiatives across global organizations. Her accomplishments include helping identify and disrupt sophisticated nation-state cyber threats, building cybersecurity programs supporting major United Technologies divestitures, leading enterprise ransomware resilience initiatives, and directing cybersecurity due diligence and integration efforts for M&A portfolios.

A recognized leader in emerging technologies, She has designed and implemented AI security and governance frameworks that enable organizations to securely adopt Generative AI and Agentic AI capabilities while aligning with regulatory, privacy, and risk management requirements. She regularly advises executives and boards on cyber risk, AI security, cloud transformation, Zero Trust, and business resilience strategies.

Ian Schenkel

Ian Schenkel

VP of EMEA & APAC, Intel 471 (UK)


Ian Schenkel is a commercial leader in cybersecurity with a track record of scaling high growth SaaS organisations across EMEA and APAC. As both a VP and founder, he has built and led global go to market functions, consistently delivered triple digit growth and secured complex enterprise partnerships across government, financial services and critical infrastructure sectors.

Ian has worked closely with security leaders in organisations including major banks, multinational enterprises, and public sector bodies, helping align commercial strategy with real world security outcomes. His experience spans threat intelligence, advanced detection, and managed security services, giving him a practical understanding of the challenges businesses face when balancing risk, operational resilience, and business priorities.

Known for his collaborative approach, Ian focuses on building trusted relationships between security, technology, and commercial teams to drive sustainable outcomes. He is a regular speaker on scaling cybersecurity businesses and fostering stronger alignment between vendors and the organisations they serve.

Ivan Milenkovic

Ivan Milenkovic

VP Cyber Technology Risk, Qualys (UK)

James Mason

James Mason

Physical Pen Tester (UK)

James Mason – is a physical pen tester with almost 15yrs experience of social engineering and breaching some of the world’s largest and most sensitive organisations.

James is a passionate advocate of physical exercising and social engineering, never forgetting that the main aim is to rapidly improve enterprise-wide resilience, while empowering staff and security awareness.

Jason O'Hare

Jason O'Hare

Northern Europe CISO, L'Oréal (UK)

Jason has been with L’Oreal for the last 8 years, currently holding the position of CISO for Northern Europe and Africa.  Joining the business during time of significant change in 2018, the business has continued to evolve in the fast-moving consumer goods industry.  The highly diversified brands, omni-channel distribution strategy and class-leading innovation – the role remains as exciting today, as it was during the introduction of GDPR.

Before working at L’Oreal, Jason provided consultancy services for several companies in the energy, finance, and transportation industries.  Was a founding member of three start-up companies and had over two decades of experience working for the UK Government.

Javier Checa

Javier Checa

CISO - Continental Europe, Equifax Iberia (Spain)

Javier Checa is the Chief Information Security Officer for Continental Europe at Equifax, where he leads cybersecurity strategy across the region and sits at the intersection of security, enterprise risk, and regulatory compliance. With over 20 years in the field, he is a recognised expert in cybersecurity risk management and the evolving European regulatory landscape — from DORA and NIS2 to the EU AI Act.

Earlier in his career, Javier honed his craft at top-tier consultancies including Capgemini, CGI, and BT, advising organisations on complex security challenges. Before joining Equifax, he went on to lead identity & access management (IAM) and secure software development (SSDLC) programmes at El Corte Inglés, one of Europe’s largest retailers, combining deep technical grounding with a pragmatic, business-focused approach to building resilient security organisations.

John Chisum

John Chisum

Vice President, Solutions Consulting, Mastercard

John Chisum is a technology and cybersecurity leader at Mastercard with expertise in network architecture, telecommunications, and secure enterprise infrastructure. He has led complex, large-scale initiatives focused on strengthening resilience, managing cyber risk, and modernizing critical network environments.

John works closely with CISOs and executive leaders to align security architecture with enterprise risk and business objectives, helping organizations make informed decisions around infrastructure investment, operational resilience, and evolving cyber threats. Known for translating complex technical challenges into clear, executive-level insights, he brings a pragmatic, business-focused perspective to cybersecurity strategy and risk management.

Jorge Fernandes

Jorge Fernandes

CISO, DPO and Director of the Internal Control Office, CMVM, the Portuguese Securities (Portugal)

Jorge Fernandes is the CISO, DPO and Director of the Internal Control Office at CMVM, the Portuguese securities supervisor. He holds a bachelor’s degree in computer science and several certifications in information security and data protection.

Jorge has more than 20 years of professional experience in Information Security in the financial services sector. His experience as CISO includes the European Securities and Markets Authority and the Council of Europe Development Bank. He is currently a member of several European regulatory groups regarding cybersecurity, operational resilience, and the digitalisation of the financial sector.

Jorge Pinto

Jorge Pinto

Information Security Specialist, Siemens (Portugal)

I’m a Computer Engineer working in information security. Over the last 27 years, I’ve been involved in a range of security projects across different sectors, helping organizations think more clearly about risk, strengthen their security programs, and prepare for incidents when they happen. I hold CISSP, CISM, CISA, and CRISC certifications and try to stay current with the field as it evolves. I’m also part of the local digital community: BSidesLisbon organizer, founding member and former president of AP2SI, member of the local ISOC chapter and D3 – Defesa dos Direitos Digitais. I care about cybersecurity, privacy, and an open internet, and I try to contribute to a more informed and resilient digital society.

Marcin Roth

Marcin Roth

Senior Cyber Security Manager, Currys (UK)

Marcin is a Senior Information Security Manager at iD Mobile, Currys’ telecoms business. He has around 15 years of experience in the IT and Information Security industries, working across the Public and Private Sector. He advises and consultants internally within the business, managing relationships with cross-functional teams and acting as a key cyber security stakeholder for new projects, programmes and initiatives. In performing a GRC function, he ensures adherence with compliance and regulatory obligations as well as supporting work around organisational governance, risks and controls.

  • Marcin has presented at a number of UK and international cyber security leadership and practitioner conferences, summits and events.
  • Marcin holds a law degree (LLB), is a Fellow of the Royal Society of Arts and has Memberships of the Chartered Management Institute, the Institute of Leadership and the British Computer Society
Maril Vernon

Maril Vernon

Field CISO, Anecdotes (USA)

Maril Vernon is a field executive and Field CISO at Anecdotes, where she helps organizations move beyond checkbox compliance into operational, intelligence-driven security. With roots in offensive and cloud security, Maril brings an attacker’s perspective into the boardroom: translating real-world threat behavior into decisions that actually hold up under scrutiny. She has worked across enterprise and highly regulated environments, advising on how to scale security programs that are not just audit-ready, but reality-ready.  Her current focus is on defining and advancing GRC Engineering and Data Controls Intelligence as a new standard for how modern organizations understand, operationalize and manage risk. 

Mark Flegg

Mark Flegg

Senior Director of Technology, CSC

Mark Flegg, CSC global director of security services, is responsible for advising a global client base on digital risk and the preventative measures brands can take to safeguard their digital assets. During his 18-year career, Mark has acquired a wealth of experience in cyber security technology focusing on domain management systems, domain name systems (DNS), digital certificates SSL (TLS), and distributed denial of service protection software and mitigation. To raise awareness of digital threats to businesses, Mark regularly presents programs dealing with domain security and cyber security assets at leading industry conferences and events.

Martin Riley

Martin Riley

Chief Technology Officer and Board Director, Bridewell (UK)

Martin Riley is the Chief Technology Officer and a Board Director at Bridewell, where he is responsible for driving continued growth and development within their Managed Security portfolio. In these roles, Martin has defined and delivered a range of Bridewell’s core services including: Cyber Threat Intelligence, Offensive Testing, Security Operations and Managed Detection and Response.

Prior to joining Bridewell in 2021, Martin held other C-Suite positions where he was responsible for the strategic direction and service development within several service providers. With 20 years’ experience in designing, implementing and leading on secure networking solutions across on premise, public, private and hybrid cloud services, Martin also brings significant expertise in digital transformation.

Michael Beaupre

Michael Beaupre

3X Global CISO / Founder, RpC Services GmbH (Germany)


Michael is a technology leader with 28+ years of experience guiding international organizations, businesses, and mid-sized firms. He is a thought leader in cybersecurity, risk management, and IT compliance with over a decade of experience as a CISO.

Michael is focused on advising businesses worldwide, ranging from 20 to 220,000 employees and has led diverse organizations in 14 industries saving over 100 million in costs.

Passionate about mentorship, he’s from the USA, based in Germany, and committed to helping CISOs see their families more by building strong coalitions of international partners.

Michael Colao

Michael Colao

CISO / CSO and Chief Underwriter - Direct and Indirect Risks, (UK)

Experienced CSO/CISO and Cyber Underwriter with than 25 years experience in financial services. Has a strong side-interest in computer forensics and in the management of digital evidence. Graduated from the Massachusetts Institute of Technology (MIT) in 1987 where he studied Mathematics and Computer Science. He has since lived in three continents and has lectured globally on security technology issues. Since 1996 has been working in Security and Technology in Financial Services primarily in London.

Munawar Valiji

Munawar Valiji

Group Chief Information Security Officer, Close Brothers (UK)

Seasoned FTSE 250 cyber and security professional with large brand and multi sector experience. Responsible for designing, implementing, and overseeing comprehensive cybersecurity strategies to safeguard organizational sensitive data and technology assets. Recognises that great outcomes are delivered by brilliant teams! Munawars skills include: Proven ability as a team leader and motivator having developed and delivered global risk and governance frameworks whilst working with multi disciplined teams of permanent, contract and consultants. Specialties: Audit, Internal Controls, Risk Review and MIS, Business Development, Vendor Management, RFP, Due Dilliegence, Information Security Management, Staff Management, IT Risk Management, Internal Audit, Compliance, Relationship Management, Analysis, Budgeting, Training, Global Liaison, Recruitment, Client Relationship Management, Project team organisation.

Ned Farmer

Ned Farmer

Geopolitical Risk | Intelligence | International Affairs | Global Security (USA)

Ned is the founder of Niebla Partners, a boutique geopolitical and security risk consulting firm. Prior to launching the firm, he managed a globally dispersed strategic intelligence team in support of a major technology company engaged in the hyper-scaling of data centers and artificial intelligence. He also led global intelligence and security programs for Transocean, a world leader in offshore drilling. Previously, as Geopolitical Risk Manager at American Airlines, he designed and implemented the enterprise geopolitical risk and security intelligence program. A recognized industry leader, Ned has served in a variety of leadership positions within the U.S. Department of State’s Overseas Security Advisory Council (OSAC).

His foundational career includes experience at Shell, the Inter-American Development Bank, the U.S. Congress, and Morgan Stanley. Ned received his B.A. in Political Science from McGill University in Montreal and his M.A. in International Affairs from American University in Washington, D.C., complemented by studies at the Universidad de Salamanca in Spain. He is fluent in Spanish, proficient in French, and has traveled to over 100 countries.

Nikolas Oelkrug-Alders

Nikolas Oelkrug-Alders

CISO, ARZ Haan AG (Germany)


Nikolas Oelkrug-Alders is Chief Information Security Officer of ARZ Haan AG, a regulated provider of financial services, billing and software to the German healthcare sector, primarily pharmacies. Reporting directly to the Management Board, he leads the group’s information security and governance agenda, with a current focus on operational resilience and DORA, AI Governance and securing the software and cloud stack. He brings a deliberately multidisciplinary background, having worked across technology research, aerospace, power generation and financial services before moving into security leadership. Canadian and US-American by background and based in Germany.

Nuno Martins da Silveira Teodoro

Nuno Martins da Silveira Teodoro

Global Cybersecurity Director, Hovione (Portugal)

Nuno Martins da Silveira Teodoro brings hands-on and executive cybersecurity leadership across Big Four consulting, fintech startups, and Fortune 500 organizations. He has built information security teams from scratch and driven high-maturity programs across ISO, NIST, PCI DSS, and GSMA standards. His experience spans cloud migration, SOC and CSIRT creation, vulnerability management, and executive-level regulatory engagement. Currently acting Vice President for Group Cybersecurity at Solaris SE, he previously held global CISO roles at Truphone and senior leadership positions at Huawei, Vodafone, and Allianz and more recently as Group Director of Technology, Vice President Group Cyber Security, Solaris SE. 

Lady Olga Maitland

Lady Olga Maitland

President, Defence and Security Forum (UK)

Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.

Paul Colnan

Paul Colnan

CISO, NewDay (UK)

Paul Colnan is the CISO at NewDay, financial services. Paul has 15 years of cyber security experience, including advising some of the world’s largest brands and he works with the board to enable secure and trusted commerce. He has an ‘ethical hacker’ background, which helps him tackle complex security issues, but he also cares about driving effective change through clear leadership and communication.  Paul has been a CISO in various sectors, including fintech, logistics, and manufacturing, and before joining NewDay he was CISO at ION, he was an Executive Director at JP Morgan Chase, where he held security roles in retail banking, M&A and cloud platform security teams. He was CISO of Revolut and Group CISO of Unipart Group. Paul likes aviation and is pursuing his private pilot’s licence in his spare time.

Phillip Davies

Phillip Davies

CISO - Europe, India and Emerging Markets (UK)

Air Commodore (Rtd). Peter Drissell

Air Commodore (Rtd). Peter Drissell

Director Aviation Security, Civil Aviation Authority (UK)

Appointed by the Civil Aviation Authority (CAA) as its first Director of Aviation Security on 1st April 2014. Peter is the Aviation Security Regulator for the UK and overseas cyber security performance of the UK aviation sector. He previously served as Director of Security & Business Continuity for the Home Office for 5 years. Prior to this, Peter had served for 32 years in the Royal Air Force from which he retired as an Air Commodore in April 2007. His last appointments were as Provost Marshal for the RAF and Commandant General of the Royal Air Force Regiment. He has been a Corporate Security Director for 20 years.

Rafael Almeida

Rafael Almeida

EU ISM, BCA (Portugal)

Rafael Almeida brings over 25 years of leadership experience across information systems, cybersecurity, and digital transformation within complex industrial and regulated environments. He began his career in systems integration and large-scale international projects, shaping his belief that sustainable security is built not only through technology, but through people, culture, and effective operating models. Over the past two decades, he has held CIO and CISO roles across the automotive, aerospace, defense, and manufacturing sectors, leading enterprise transformation programs, building high-performing international teams, and embedding cybersecurity into core business operations. His experience spans cloud adoption, cyber resilience, security operations, and risk management, with a strong focus on turning security from a control function into a business capability. Currently leading Information Security initiatives across Europe, he drives strategy across more than 20 countries, focusing on strengthening resilience, navigating regulatory challenges such as DFARS, TISAX or NIS2, and helping organizations convert cybersecurity into a measurable business advantage.

Ray Stanton

Ray Stanton

NED/ Board Advisor / CISO/CSO (UK)

An experienced Senior Leader & Corporate Executive, Security & Risk Professional, Ray is a globally acknowledged and well-known thought leader; recognised and highly respected as someone who delivers. Ray has sat on global programmes for the World Economic Forum on Cyber Resilience and the Advisory Board for the Information Security Forum. Ray has held Group CISO/CSO & EVP roles for BT, National Grid, Interoute, Redwood Technologies and Airbus UK.  He has been fortunate enough to have held global accountability, ranging from consultancy, through to design, build and run of managed services; including full profit and loss ownership for multiple business lines, while combining this experience with protection of Critical National Infrastructure in the Energy and Communications industries.

Prof Dr Robert Coles

Prof Dr Robert Coles

Chair, Audit and Risk Assurance Committee, University of Brighton (UK)

Robert has over 35 years of audit, risk and cybersecurity experience and has held a number of senior leadership positions, including CISO for the NHS and health & care system, GSK, National Grid, and Merrill Lynch and Head of InfoSec at Royal Bank of Scotland, and he was a partner at KPMG. Robert is a Senior Fellow at the Centre for Assurance Research and Engineering at George Mason University, Washington DC. He is also an Honorary Professor at UCL. He was awarded a PhD in psychology by the University of Leeds for his work on the perceptions of information and IT risk and has published and presented on this and other topics. He continues to undertake research in these areas. He was also awarded an MBA from Manchester Business School. Robert also holds a number of commercial board positions including Chair of the Crossword Consulting Ltd Board, Non-Executive Director of Crossword Cybersecurity PLC, and Chair of the Board at Think Cyber Ltd and advisor to the Government of Singapore Ministry of Health. He is also a Governor/Trustee and Audit Committee Member of the University

Simon Riggs

Simon Riggs

CISO, OneAdvanced (UK)

Recognised cyber security MD with over thirty years of industry experience implementing successful programmes in demanding global environments including investment banking, retail, media and FMCG. Simon provides strategic vision, leadership and technology expertise with a proven track record for effective risk management, change delivery and exceptional impact. He has a strong track record of creating and leading sector wide initiatives. Simon was recently interim CISO at John Lewis, McKesson UK and Avon. Prior to these roles, he was regional CISO at Bank of America Merrill Lynch for 9 years, where he had responsibility for all aspects of cyber security in the EMEA region working closely with business and technical leaders. A member of the bank’s information security senior leadership team that directs the enterprise wide prevention and response activities, Simon had an active role in defining the global strategic operating model and setting strategic long-term goals. Previous sector positions have included Bank of England’s industry chair of the Cyber Coordination Group and Chair of CPNI’s Financial Services Information Exchange (FSIE) and Global Head of IT Security at Thomson Reuters.

Salpi Stojan

Salpi Stojan

Cybersecurity Project Manager, Vivicta (Czech Republic)

Salpi Stojan is a Cybersecurity Project Manager in the Security Operations Center, leading projects from SIEM deployments and MDR/XDR integration to threat monitoring, incident response, and security governance. She’s known for turning security goals into practical outcomes and for scheduling 15-minute meetings at quirky times like 14:55 to keep things efficient and engaging.
Originally from Istanbul and now based in the Czech Republic, Salpi has lived across Europe, travelled to 20+ countries, and speaks five languages fluently. With a Master’s degree in Business Management and a Bachelor’s in Industrial Engineering, she blends analytical thinking with cross-cultural insight. A part-time cybersecurity professional and full-time mom, she mentors through Women4Cyber and never stops learning. Outside of work, she enjoys nature walks, languages, and scammer-baiting videos to explore the psychology behind social engineering.

Stefan Weber

Stefan Weber

COO Digital Platform, Deutsche Bahn Fernverkehr AG (Germany)

Stefan Weber is an experienced IT and operations leader focused on ensuring stable day-to- ay service delivery while transforming complex enterprise platforms. In senior roles—most recently as Head of Operations & Shared Services for the Sales Platform (including DB Navigator, Bahn.de)—he has led the operational transition from legacy (host/cloud) environments to a cloud-based platform, shaped interface and service agreements, and continuously evolved operating models across ITSM, DevOps, FinOps, and SecOps. His expertise combines strategic governance, sourcing, and change/release management with hands-on execution in demanding industries such as rail passenger transport, aviation, and telecommunications.

Sybil VR Kleinmichel

Sybil VR Kleinmichel

Managing Director, Sycheck Systems (Germany)


Sybil V. R. Kleinmichel is an international cybersecurity and operational resilience leader with more than two decades of experience advising global enterprises, regulators, and critical infrastructure organizations. She has served multiple times as Chief Information Security Officer and Head of Information Security, leading large-scale cybersecurity, risk, and resilience programs across highly regulated environments. Throughout her career, Sybil has worked at the intersection of cybersecurity, operational resilience, and governance, helping organizations strengthen their preparedness for complex disruptions through structured testing, incident response planning, and cross-organizational collaboration.

In recent years, Sybil has focused on advancing multi-stakeholder resilience planning and testing, bringing together public and private sector leaders to better prepare communities and institutions for systemic risks. Drawing on her experience as both a CISO and trusted advisor to senior security leaders, she advocates for resilience strategies that extend beyond individual organizations to the broader ecosystems on which societies depend.

Toks Oladuti

Toks Oladuti

Chief Information Security Officer, Dentons (UK)

Toks is responsible for the global delivery of information security at Dentons, the world’s largest law firm. He has over 20 years’ experience working in security, technology and privacy, across a number of industries.

Toks is an experienced and strategic business risk leader. He has a particular passion for strategy and team building and development.  His core skillset, developed over the years includes security operations and architecture, risk management and risk driven investment, data protection, compliance and audits, and enterprise culture, awareness and training.

Toks has contributed to the business and technology community through information sharing, groups, speaking engagements and multi-industry networking. As strong supporter of education and schools, he has provided advice in areas of security, data protection, user awareness and cloud transformation.

Tom Berry

Tom Berry

Board Advisor, NED, BeLessBeige (UK)


Tom Berry is a specialist communications consultant and board advisor. He is European Chair of the global PR agency MikeWorldWide and has worked in technology, corporate and crisis communications for 25 years. Tom is also an Independent Council Member for King’s College London, a Trustee for Onvero (The Employers’ Network for Equality and Inclusion) and was a Non-Executive Director for Mental Health First Aid England. As one of the early Advisory Board Members for ClubCISO, Tom has been deeply involved in working with CISOs and security companies to promote the profession. Before working in communications Tom was a journalist for a decade, winning Business Journalist of the Year and Magazine Journalist of the Year awards from the Periodical Publishers’ Association and The Work Foundation.

Tunde Benjamin

Tunde Benjamin

Head of Cyber, Smollan (UK)

Tunde is responsible for Information Security at Advantage Smollan, a leading Sales, Marketing & Data Company. Prior to joining he worked at Colliers International as Head of Information Security. He has also worked as a Network Engineer at KKR supporting their Infrastructure and Operations.

He holds a CISSP #765107‎ and degree in Computer Systems & Networks from Plymouth University.

Dr Viktor Polic

Dr Viktor Polic

CISO, ILO - United Nations (Switzerland)

More than two decades of professional experience in information management and governance, with particular focus on information security, risk management and assurance for large multilateral public sector organizations with global presence. Actively contributing to inter-organizational working groups for establishing policies, standards, and guidelines in the area of information security, personal data protection, awareness programs, risk analysis and metrics. Conducting research in cryptography, data protection regulation, and risk management. I’ve started professional career in information technology in the year of the release of Mosaic Web browser, Intel Pentium CPU, Microsoft Windows NT, Debian Linux, Doom computer game… Since the Internet bubble, teaching computer science and telecommunications courses as adjunct faculty at Computer Science Department of Webster University in Geneva. Actively contributing to academic program advancement as a member of the Scientific Committee for Advanced Studies in Information Security at the Department of Management Studies of the Faculty of Economic and Social Sciences at the University of Geneva. Advocating advancement in information security as an author in journals and as a speaker at professional conferences

WH

Warren Houghton

Warren Houghton – is a security professional with over a decade of experience testing, building, designing, and breaking building security systems across both the public and private sectors. His work specialises in physical security, adversary simulation, and black teaming, with a focus on how organisations prevent, detect, and respond to real-world threats. Warren has extensive experience assessing and bypassing access control systems, including research into credential security, card cloning, and weaknesses in physical authentication technologies. He has led and supported assessments across corporate environments, critical national infrastructure, and high-security sites, combining technical expertise with practical offensive security experience. His work bridges the gap between physical and cyber security, helping organisations understand not just whether controls exist, but whether they stand up to determined attackers in the real world.

Will Harvey

Will Harvey

Head of Cybersecurity (CISO), IAG Transform (UK)


Will Harvey is the Head of Cybersecurity (CISO) for IAG Transform – the company driving and innovation across IAG’s airline brands and the wider aviation industry, through expertise and capabilities in procurement, technology, AI, innovation, and transformation. Before his cybersecurity carer in aviation Will worked in several UK Government Departments running cybersecurity for some of the UK’s largest systems, coordinating cybersecurity for major international summits and events before making a shift to policy to shape UK cyber policy to public sector and critical infrastructure, driving major reforms to cyber incident management and resilience arrangements. Will has worked with tech companies, researchers and UK academia to push forward the UK’s cyber agenda.

Platinum Protector & Networking Sponsor

Dataminr

Dataminr

Dataminr has created a revolutionary AI platform for discovering real-time events, risks, and threats in public data, providing global organizations and corporations with critical and actionable information. Its pioneering multi-modal fusion AI pulls from more than one million unique public data sources to synthesize terabytes of data spanning text, image, video, audio, and sensor signals for accurate, real-time event detection across 150+ languages and 220+ countries. Dataminr pushes the boundaries of real-time information with ReGenAI — an innovation that combines Predictive AI and Generative AI to describe breaking events and provide dynamic re-generating updates to events as they unfold. Powered by more than 50 proprietary large-language models, Dataminr delivers the earliest actionable information to enhance the security and resilience of organizations, infrastructure, and people. For more information, visit www.dataminr.com.

CISO 360 Innovator

Intel 471

Intel 471

Intel 471 equips enterprises and government agencies with intelligence-driven security offerings powered by real-time insights into cyber adversaries, threat patterns, and potential attacks relevant to their operations. By integrating human-sourced intelligence with advanced automation and curation, the company’s platform enhances security measures and enables teams to bolster their security posture by prioritizing controls and detections based on real-time cyber threats. Organizations are empowered to neutralize and mitigate digital risks across dozens of use cases across our solution portfolios: Cyber Threat Exposure, Cyber Threat Intelligence, and Cyber Threat Hunting.

Our customers’ eyes and ears outside the wire.

www.intel471.com

Platinum Protectors & Networking

Mastercard Cybersecurity

Mastercard Cybersecurity

Mastercard Cybersecurity is helping organizations secure their infrastructure, applications, third parties, and global supply chains by providing deep visibility into risk across internal systems and external relationships. Through unique threat intelligence, cyber risk insights, and multi-layered, cloud-based defense technologies, Mastercard helps organizations and consumers address risk in real-time, enhancing resilience against today’s most sophisticated cyberattacks.

www.mastercard.us/en-us.html

Bridewell

Bridewell

Bridewell is a cyber security services company that specialises in protecting and transforming critical business functions for some of the world’s leading organisations.

Their consultants work with clients to deliver end-to-end services that solve their security and business challenges. Bridewell’s specialists are highly accredited by major industry bodies and have extensive experience delivering services across cyber security, managed security, penetration testing, and data privacy.

Founded in 2013, Bridewell is headquartered in the UK where it runs a 24/7 Security Operations Centre (SOC) and has a growing presence in the US to further support global clients.

For more information, visit www.bridewell.com

Qualys

Qualys

Qualys is a pioneer and leading provider of disruptive cloud-based IT, security and compliance solutions with over 19,000 active customers in more than 130 countries, including a majority of each of the Forbes Global 100 and Fortune 100. Qualys helps organizations streamline and consolidate their security and compliance solutions in a single platform and build security into digital transformation initiatives for greater agility, better business outcomes, and substantial cost savings. The Qualys Cloud Platform and its integrated Cloud Apps deliver businesses critical security intelligence continuously, enabling them to automate the full spectrum of auditing, compliance, and protection for IT systems and web applications across on premises, endpoints, cloud, containers, and mobile environments. Founded in 1999 as one of the first SaaS security companies, Qualys has established strategic partnerships with leading cloud providers like Amazon Web Services, Microsoft Azure and the Google Cloud Platform, and managed service providers and consulting organizations including Accenture, BT, Cognizant Technology Solutions, Deutsche Telekom, DXC Technology, Fujitsu, HCL Technologies, IBM, Infosys, NTT, Optiv, SecureWorks, Tata Communications, Verizon and Wipro. The company is also a founding member of the Cloud Security Alliance.

www.qualys.com

Dataminr

Dataminr

Dataminr has created a revolutionary AI platform for discovering real-time events, risks, and threats in public data, providing global organizations and corporations with critical and actionable information. Its pioneering multi-modal fusion AI pulls from more than one million unique public data sources to synthesize terabytes of data spanning text, image, video, audio, and sensor signals for accurate, real-time event detection across 150+ languages and 220+ countries. Dataminr pushes the boundaries of real-time information with ReGenAI — an innovation that combines Predictive AI and Generative AI to describe breaking events and provide dynamic re-generating updates to events as they unfold. Powered by more than 50 proprietary large-language models, Dataminr delivers the earliest actionable information to enhance the security and resilience of organizations, infrastructure, and people. For more information, visit www.dataminr.com.

Platinum Protectors

Kovrr

Kovrr

Kovrr financially quantifies cyber and AI risk. Kovrr’s quantification platform empowers enterprise decision-makers to manage exposure across cyber and AI domains more effectively by delivering in-depth risk analyses that drive actionable, financially justified decisions aligned with broader business goals. Regardless of an organization’s current framework, model, or risk register, Kovrr leverages existing data and elevates the level of insight. Our enterprise-ready solution provides security, risk, and GRC teams with a granular assessment that can be communicated confidently at the highest organizational levels. Founded in 2017, Kovrr is led by a team of (re)insurance professionals, cyber and AI risk modelers, intelligence experts, and experienced software developers.

https://www.kovrr.com/

Torq

Torq

Torq is the AI SOC platform that combines agentic insights and automation so that enterprises can triage, investigate, and respond to actual risks, faster. Working alongside your SecOps team, Torq streamlines every step from alert through resolution. The platform analyzes your risk context to identify your biggest threats and integrates with your entire security stack to turn alerts into action.
https://torq.io/

Emerald Enforcer

CSC

CSC

CSC is the trusted security and threat intelligence provider of choice for the Forbes Global 2000 and the 100 Best Global Brands® with focus areas in domain security and management, along with digital brand and fraud protection. As global companies make significant investments in their security posture, our DomainSecSM platform can help them understand cybersecurity oversights that exist and help them secure their online digital assets and brands. CSC also provides online brand protection—the combination of online brand monitoring and enforcement activities—with a multidimensional view of various threats outside the firewall targeting specific domains. CSC is a global company capable of doing business wherever our clients are—and we accomplish that by employing experts in every business we serve.

www.cscdbs.com

Innovator Sponsors

Validato

Validato

Validato provides an unbiased assessment of an organisation’s ability to defend against adversary behaviours related to known threats, as described in the MITRE ATT&CK knowledge base.
https://validato.io

Intel 471

Intel 471

Intel 471 equips enterprises and government agencies with intelligence-driven security offerings powered by real-time insights into cyber adversaries, threat patterns, and potential attacks relevant to their operations. By integrating human-sourced intelligence with advanced automation and curation, the company’s platform enhances security measures and enables teams to bolster their security posture by prioritizing controls and detections based on real-time cyber threats. Organizations are empowered to neutralize and mitigate digital risks across dozens of use cases across our solution portfolios: Cyber Threat Exposure, Cyber Threat Intelligence, and Cyber Threat Hunting.

Our customers’ eyes and ears outside the wire.

www.intel471.com

Anecdotes

Anecdotes

Spoiler alert: you’re about to fail. Again. You’re not going to know if your policies are actually being implemented, you won’t have a clear view of your risk posture, and forget about achieving continuous compliance. An enterprise GRC program running on traditional technology is gonna disappoint 100% of the time. Traditional is where GRC goes to die.
‍
To manage GRC today, you need more than just automation—you need a revolution. You need a continuous flow of data, collected directly from your organization’s systems, and AI that assists with everything from collecting that data to automatically testing and monitoring it in the context of each use case.
‍
Anecdotes’ AI-native GRC platform is built on a foundation of complete, accurate, and structured data, automatically collected from your systems and trusted by the world’s largest enterprises and auditors. With AI embedded across every task—audits, risk management, continuous control monitoring, and everything in between—you can finally do GRC right.

www.anecdotes.ai

ThreatLocker

ThreatLocker

Supporting Organisations

AP2SI

AP2SI

AP2SI (Portuguese Association for the Promotion of Information Security) is a non-profit organisation dedicated to advancing cybersecurity and information security in Portugal. Through partnerships, awareness initiatives, and professional development programmes, AP2SI supports individuals and organisations in addressing emerging digital challenges with confidence and resilience. By fostering collaboration and knowledge sharing, AP2SI contributes to a safer and more trusted digital environment for society and business alike.

Information Security Forum

Information Security Forum

Founded in 1989, the Information Security Forum (ISF) is an independent organisation that is driven by its Members – ranging from Fortune 500 and Forbes 2000 listed corporations, to public-sector bodies and government departments.

Our business-driven solutions provide organisations with the guidance, tools and methodologies needed to tackle the wide-ranging governance, risk and compliance challenges impacting businesses around the world today.

For more information, visit: www.securityforum.org/

To enquire about Sponsorship opportunities please contact sponsorship@pulseconferences.com.

CISO 360 Conferences – A Unique Sponsorship Proposition

  • One-to-one meetings – pre-arranged with preferred prospective clients on an end-to-end basis for your team
  • Fully integrated – as a valued partner, we ensure that you are integrated into the fabric of the event experience
  • Bespoke curated space – benefit from bespoke conference packages without the big cost of hosting your own event
  • You’re invited! Networking dinners, boat cruises, cultural group visits are integral to the CISO 360 conference experience. There is no ‘them and us’
  • Consultative and collaborative – we work with you on the content, messaging and practicalities from initial sign-up to onsite execution through to post-event follow up
  • Connect in a meaningful way with new contacts as well as existing clients – leave the event with a wealth of new connections and professional friends. Free client places
  • Innovate your market offering with CISOs – engage in a proactive, two-way dialogue with CISOs to improve your offering and approach. Our CISO community like to help!

What do CISO 360 Sponsors say? 

“The key take-away of CISO 360 is the calibre of the individuals who attend. I’ve done these events over many years and I’m incredibly impressed with the team. They pulled this off brilliantly! I’ve had conversations with people who have budge, make decisions and who want to know about cybersecurity technologies that Mastercard cyber intelligence has.”
John Quinn, EMEA Strategic Alliances Director, Mastercard

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”
Gary Penolver, CTO, Quod Orbis

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”
Dr. Alex Jaimes, Chief Scientist and SVP of AI, Dataminr

“We aren’t just doing this Pulse event but we did their New York event at the beginning of the year and we are also signed up to the CISO 360 in Singapore later this year. For me this has been a great opportunity to introduce our CEO, Stephen Cavey, to Pulse and to meet the CISO communities. We’ve come away with some great follow up opportunities – a super event!”
Head of Global Marketing, Ground Labs

“Pulse has exceeded expectations again in terms of the event they put on, the content and very much the important factor for us is on the social side where we get to socialise with CISOs on boat trips!”
Matt Middleton-Leal, Managing Director, EMEA, Qualys 

“With normal events that we attend, its fleeting and you only get moments with your colleagues. You don’t really have an opportunity to spend quality time or have the bandwidth to go deep into topics and subject areas. CISO 360 does this in a very  unique way.”
Torquil Macleod, Director, Via Resource

“Pulse put on what was the impossible, nearing the end of covid restrictions It’s been an amazing experience. Fantastic delegates. Conversations have been brilliant, it’s a great event for us, thanks”
Ross Brewer, General Manager & Vice President – EMEA & APJ, AttackIQ

“Pulse creates a unique environment for us to interact with the senior leadership team in our customer base and to prospect around new clients. Because of the unique environment people are much more open to talking and discuss issues. If this was a formal business environment it would be impossible for us to do that so thanks. It’s a fantastic event for us!”
Matt Middleton-Leal, Managing Director EMEA North, Qualys

“First and foremost, you know what you’re going to get with Pulse, the quality of delegate is always high. The agenda is very relevant. Finally, it’s great to be back face to face to build relationships. A thoroughly successful event for us!”
Dan Panesar, Director UK & Ireland, Securonix

“This is our first time at a Pulse event. It’s been a very positive experience. Fantastic to be face to face with customers. Great to have 1:1 meetings. Really insightful talks and the acceleration in digital transformation, one we’ll do again!”
Mark Lavis-Jones, Director Enterprise Cyber, QinetiQ

“This is our first time at a Pulse CISO 360 event. What a fantastic event! Great to get together and we’ve had very effective quality meetings. Great content with workshops and breakout sessions. I look forward to many more in the future”.
Richard Fridge, Regional Sales Manager, HUMAN

“2.5 days to mix with delegates allows both parties to determine whether any business is to be done and to develop personal relationships. We generated and qualified many leads which stand a good chance of leading to business. What went well: – understanding what customers want: a product of spending time with them – quality of delegates: as good as any event but the key difference was the amount of time spent listening to them and the opportunity to socialise. – quality of support from Pulse: very happy!”
Head of Commercial Business Development, Garrison

“Pulse Conferences’ events – the most informative, interactive and engaging event I have ever participated in.”
EMEA Platform Director, SailPoint

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.”
Director, SailPoint

“This was our first but definitely not our last CISO 360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.”
Director, NetClean

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one!”
Director, Synack

“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.”
Director EMEA, SailPoint

“Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.”
CMO, Company85 (now Telstra Purple)

“Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a beneficial and enjoyable experience!”
CMO, Blueliv

“I found CISO 360 Congress to be a great place to share ideas about current and future problems.”
Head of Section, GMV

“Excellent conference, brilliantly put together!”
Partner, Bridewell Consulting

Sponsorship Opportunities

To find out more about sponsorship opportunities for  11th CISO 360 Global Congress please contact:
sponsorship@pulseconferences.com

Who Joins?

By Designation

  • Chief Information Security Officer (CISO)
  • Chief Security Officer (CSO)
  • Director / Head of Cybersecurity
  • Director / Head of Cyber Threat Intelligence
  • BISO / CIRO
  • CTO, CIO, CRO
  • Chief Security Architect / Senior Security Architect
  • Director / Head of Security Infrastructure
  • Director / Head of Networks, Applications, Cloud
  • Director / Head of Technology Innovation
  • Director / Head of Digital Risk
  • Chief Data Officer
  • Chief Privacy Officer

By Sector – example

  • Financial Services – including Insurance
  • Energy – power, water and critical national infrastructure companies
  • Extractives – mining, oil and gas
  • Pharmaceuticals and health
  • Consumer goods
  • Manufacturing
  • Retail
  • Transport and logistics
  • Government departments

Venue and Accommodation 2027

The new venue for the 11th CISO 360 Global Congress 2027 will be announced in the coming months.

The 10th edition was hosted at:

📍Palácio Estoril
R. Particular  2769 – 504 Estoril
Cascais | Lisbon | Portugal

PAST VENUE: JUNE 2026
A TIMELESS HISTORICAL OASIS OF ESTORIL, ONLY A 30-MINUTE DRIVE FROM LISBON CENTRE

Palácio Estoril
Cascais | Lisbon | Portugal

On the sunlit Cascais coast, just outside Lisbon, the Palácio Estoril offers nearly a century of elegance, discretion and quiet significance. Estoril is no ordinary setting. Befittingly, during WWII, the hotel became a neutral crossroads for intelligence networks – with Allied agents based at the Palácio while rival operatives occupied nearby hotels. In 1968, James Bond stayed here during the filming of On Her Majesty’s Secret Service, where reality and legend briefly converged.

A decade of practitioner-led trust deserves a venue defined by discretion, strategy and global perspective. A place where history was shaped quietly behind closed doors.

Ten years on, we gather somewhere worthy of the milestone 10th CISO 360 Global Congress.

Accommodation Savings

The discounted accommodation block we secure will be announced in due course.

PAST VENUE: 2026
A Grand Setting for the World’s Leading Cyber Security Minds

The 10th CISO 360 Global Congress will be hosted in the iconic Grand Atlantic Ballroom at the Palácio Estoril Hotel, one of Portugal’s most prestigious and storied event venues. The Atlantic Ballroom is bathed in natural light from sweeping windows that overlook the hotel’s manicured gardens, creating an atmosphere that is both inspiring and sophisticated. The space has hosted countless prestigious national and international events, and it provides the perfect stage for the high-calibre keynotes, panels, and presentations that define the CISO 360 experience.

Networking Hub
Directly connected to the Grand Atlantic Ballroom, the dedicated CISO 360 Networking Hub has been designed to make every connection count. It serves as the beating heart of the congress, a curated space for peer-to-peer dialogue, and inspiring conversations.

Outdoor Terrace & Lawn
Beyond the ballroom, delegates are invited to take full advantage of the hotel’s spectacular outdoor spaces. The sweeping terraces surrounding the gardens offer an elegant setting.

VenueVenueVenueVenueVenueVenueVenueVenueVenueVenueVenueVenueVenueVenue

Registration details

Tier 1: – Delegate
In-house Security Practitioner
£495

Delegate Registration for 2027

Available to book by CISOs and practitioners – i.e. persons who are doing the role of CISO, CSO, cyber threat intelligence professional, risk managers or other in-house executives roles.

*This offer does not apply to persons working in marketing, sales, business development or general management roles for companies providing advisory services or solutions to the security community. Exceptions may apply for CISOs and senior practitioners working for these types of companies who are actually doing the day to day job of securing their organisation. Pulse Conferences reserves the right to approve that registration is under the correct tier. All Attendees at the event must be pre-registered online and pre-approved at the sole discretion of Pulse Conferences.

Tier 2 – Networking Pass
Providers, Advisors, Consultants
£1,995 +20% UK VAT

We have set aside a limited number of Networking Passes, designed for executives working at Providers, Vendors, Resellers, Distribution companies. Through this type of participation sponsorship, Executives can still benefit from the business development and promotional opportunity of attending even if their companies are unable to commit to a fully branded Sponsorship this year. This is an opportunity to send Executives to network with participants, to meet new prospective customers and to join the discussions – with a view to fuller sponsorship at future Pulse conferences!

Tier 3: Are you are confirmed Speaker, Sponsor or Supporting Association?

Please use this link if you are already a confirmed participant of the event – whether you are a Speaker, Sponsor or Supporting Association.

Inclusions

  • Entry to Participate:  Join the 11th CISO 360 Global Congress & Roundtable(23-25 June 2027) 
  • Evening Networking Activities: An integral part of the CISO 360 experience. All participants are invited. Wine-tasting and tour, Dinner at a vineyard, Catamaran coastal cruise receptions, seafood dinner
  • Lunches, coffee and daily refreshments: All included throughout the 2.5 days
  • Live Translation: Access to live translation captions in Portuguese, Spanish, French + other languages available on your device via the event app
  • CISO 360 WhatsApp Group: Exchange insights and share feedback with fellow CISOs onsite (limited to CISOs / practitioners only)
  • Event Materials: Speaker Slides, Photos, Photo Gallery (subject to speaker opt-out)
  • CISO 360 Gift from Pulse, prize draw and branded give-aways
  • Certificate of Attendance: Softcopy upon request
  • CPE / CPD Accreditation: Attendance at this Pulse Conferences event qualifies for Continuing Professional Education (CPE/CPD) credits. Delegates may claim hours toward relevant professional certifications. Delegates may claim up to 18 CPE/CPD credits for full participation over the 2.5-day educational programme
  • Security 360 Circle: Invitation to join regular virtual roundtables led by practitioners and subject matter specialists on key security, intelligence, resilience topics
  • Member of the Pulse Community: Be part of the CISO + CSO 360 community for future event invitations

Exclusions

  • Travel and accommodation and all other costs associated with planning for / joining the event

Worldwide Terms and Conditions
For purposes of these Terms “Attendee” shall mean all participant types at the event (Speakers, Sponsors, Delegates, Guests, Partners, Supporting Associations).  By participating in this Event, you agree to these Terms.

Payment Policy

  • Any payment is due in full at the time of registration. Inclusions and exclusions are listed. Your registration will not be confirmed until payment is received and may be subject to
  • cancellation.
  • All ‘Early Bird’ Discounts must require payment at time of registration and before the cut-off date in order to receive any discount.
  • Any discounts offered whether by Pulse Conferences (including team discounts) require payment at the time of registration.
  • Discounts cannot be used in conjunction with other offers.

Methods of Payment

  • Credit Card – All major credit cards are accepted online. Credit card details will not be accepted via email, phone. Pulse does not store any financial details.
  • Bank Transfer – Please ensure when paying via Bank Transfer that the invoice number is referenced and a copy of the remittance is emailed to accounts@pulseconferences.com. All bank charges are to be borne by the sender.

Cancellation, Postponement and Substitution Policy

  • You may substitute a Delegate at any time by providing notice to Pulse Conferences. Please let us know the details of your replacement copied into an email introduction.
  • For cancellation of an in-person Delegate place, if a hybrid option exists, you will automatically be transferred to become a virtual Delegate.
  • No credit will be issued for any cancellations occurring within seven (7) days (inclusive) of the event. This also includes on the day cancellations, or Delegates who cannot stay for the event duration. Only a valid doctor’s note will entitle you to a 100% credit to be used at another Pulse event which must occur within one year from the date of issuance of such credit.
  • For any cancellations received in writing not less than eight (8) days prior to the event, you will receive a 90% credit to be used at another Pulse event which must occur within one year from the date of issuance of such credit. An administration fee of 10% of the contract fee will be retained by Pulse Conferences for all permitted cancellations.
  • For any cancellations received in writing not less than 60 (sixty) days prior to the event, you will receive a 100% credit to be used at another Pulse event which must occur within one year from the date of issuance of such credit. If the Delegate is unable or unwilling to attend another event, then you will receive 90% refund of the fee paid.  All refunds will be processed within 2 weeks minus a 10% administration / transaction cost fee that will be retained by Pulse Conferences for all permitted cancellations.
  • Should Pulse Conferences postpone an event for any reason, you will receive a credit for 100% of the fee paid. You may use this credit either for the same event on the new date or for another event, which must occur within one year from the date of cancellation. If the Delegate is unable or unwilling to attend the new date or another event, then you will receive 100% refund of the fee paid.
  • Should Pulse Conferences cancel an event for any reason, you will receive a credit for 100% of the fee paid. You may use this credit for another event, which must occur within one year from the date of cancellation. If the Delegate is unable or unwilling to attend another event, then you will receive 100% refund of the fee paid.
  • Except as specified, no credits will be issued for cancellations. There are no refunds given under any other circumstances. Pulse Conferences is not responsible for any loss or damage as a result of a substitution, alteration or cancellation/postponement of an event.
  • Please note that Pulse Conferences reserves the right to alter or modify the advertised speakers and/or topics if necessary without any liability to you whatsoever. Any changes to the programme will be updated on our website.

Code of Conduct
Pulse Conferences events are intended for networking, collaboration, thought-leadership and to provide inspiration amongst the security community. We generally assume that most people are intelligent and well-intended and we are not inclined to tell people what to do. Ensuring the positive and fulfilling experience of each participant in our community is our top priority. 

Accordingly:

  • All participants are expected to show respect and courtesy to others by abiding by this Code of Conduct to participate in our community.
  • Pulse is dedicated to providing an inclusive and harassment-free experience for everyone, regardless of gender, gender identity and expression, age, sexual orientation, disability, physical appearance, body size, race, ethnicity, national origin, religion (or lack thereof), or other choices.
  • We do not tolerate harassment of or threats (verbal or physical) to our community in any form. Sexual or discriminatory language and imagery is not appropriate for any of our events or for online media.
  • Attendees must refrain from abusing alcohol or substances during the event including the official networking event. Any violation of this policy will result in immediate removal from the event.
  • Community participants violating these rules may be sanctioned or expelled from current and/ or future events or venues at the discretion of Pulse Conferences, and without a credit or refund.
  • Pulse Code of Conduct applies during all hours of the event programme as well as during the official networking events that are also part of the event.
    Please bring any concerns during the event to the immediate attention of our team by emailing teampulse@pulseconferences.com or by calling or texting +44 (0)203 455 9444.

Health and Safety

  • In-person events hosted by Pulse Conferences are organised in accordance with the latest health and safety regulations, guidelines, and recommendations, as directed by the Center for Disease Control and Prevention, World Health Organization, and the government of the host country of specific events. Working with its venues and suppliers, Pulse takes appropriate health and safety measures. Health and Safety measures for each event will be communicated online and in the specific event information that all registered Attendees receive.
  • Pulse Conferences also counts on your commitment.  As an attendee, you agree to comply with the following measures: Do not attend the event if you have covid-19 or if you are generally feeling unwell at the time of the event. 
  • Please acknowledge that participation in events and in-person activities brings some risk and you assume responsibility for your own well-being.

Force Majeure
Pulse Conferences has the right to virtualise the programme, postpone the date or change the location of the event, if delay of performance is caused by circumstances or events outside of its reasonable control, which shall include but not be limited to industrial action, acts of God, terrorism, pandemic, power cuts or internet failure, civil commotion, refusals to grant licenses or permissions.

Indemnity
By registering, the attendee hereby indemnifies and holds Pulse harmless from and against any and all costs, damages and expenses, including legal costs, which are incurred by the client in such a scenario whereby the event is delayed, changed or virtualised due to circumstances outlined above in the force majeure. We advise booking travel or accommodation that is flexible or refundable. In no event shall Pulse Conferences be liable for any claim, loss, liability, damage or cost to persons or property arising from attendee participation in this event.

Use of Multimedia
Attendees are encouraged to capture their own event experiences in the permitted areas of the event venue, provided it does not defame other event attendees or infringe on copyrighted branding and content. Pulse Conferences leverages social media to post photos and videos to its social media feeds during the event.

By attending the Event, you acknowledge and agree that:
Pulse Conferences may edit and use the footage it captures at Pulse Conferences’ events for promotional activities in the course of its business. If you prefer not to be included in footage captured by Pulse Conferences, please let us know in writing before the event teampulse@pulseconferences.com or by calling +44 (0)203 455 9444.  Or if you are onsite, you visit the Pulse registration desk upon your arrival. A unique badge will be provided for you. Pulse Conferences disclaims all liability for the capture of your image by attendees in any multimedia format at the event (mobile recording devices).

Pulse Conferences Privacy Policy

To read about Pulse Conferences Privacy Policy and download in pdf format please click below.

Download Pulse Conferences Privacy Policy here

Testimonials – CISO 360 Global Congress

“This event is not driven by sales pitches; it is genuinely about connecting with people. The community is very welcoming, knowledgeable and kind, the venue was incredible, and the post-session events provided excellent opportunities to exchange impressions. This event fostered reflection and progress in my career. I look forward to seeing all these amazing people at the next event!”
Michael Matias, Senior Expert Cybersecurity Architect, External Contractor at European Commission

“It was a real pleasure to join you in Estoril this year. I met a lot of great people and had genuinely valuable discussions – open and meaningful in a way that is rare at events like this.”
Nikolas Oelkrug-Alders, CISO, ARZ Haan AG – Germany 

“Excellent atmosphere to share knowledge and experiences with your counterparts.”
Javier Checa, CISO, Equifax – Spain

“Awesome Conference! Knowledgeable people leading to great advice through collaboration. The network is fantastic!”
Jorge Pinto, Information Security Specialist, Siemens – Portugal

“What a fabulous event. Very insightful with lots of content to apply to our organisations”
Jason O-Hare, Northern Europe CISO, L’Oreal – UK

“10 years and still as fresh, interesting and vibrant as the 1st”
Brian Brackenborough, CISO, London Metropolitan University – UK

“This was one of the best security events I have ever attended. Inspiring professional, thought-provoking topics and flawless organisation. An outstanding experience”
Raf Almeida, EU ISM, BCA / CAG – Portugal

“This has been the best CISO 360 Global Congress yet! With so many CISO peers sharing best practices and knowledge, I have many new ideas about practical current thinking on resilience, methods, tools, TPRM and AI risk management that I can implement and new insights into the speed of change and what to automate. Peers I can call when in need!”
Sybil Kleinmichael, CISO – Germany

“Excellent conference with lots of knowledge, shared opinions to apply across organisations”
Eng. Luis Anselmo, Head of Information Security, Celfocus, SA – Portugal

“Amazing event bringing back lots of ideas and questions!”
Rui Pires, Cyber Security Engineer, Nokia – Portugal

“Enjoyed the open and honest exchange among all participants”
Ives Laaf, CISO, adesso – Germany

“One of the best conferences I have attended in the last 5 years. The speakers and topics covered in the conference were spectacular”
João Alves Monteiro, Security Business Manager, Logista – Portugal

“These CISO 360 events are very important and well organised. This was my third time, and it’s amazing to see this community growing, new and familiar faces”
Sérgio Gonçalves, CSO, Logista – Portugal

“Warm environment to discuss hard problems”
Ana Respicio, Professor, Universidade de Lisboa – Portugal

”This congress was one of the best events I have attended. It could be even better with more technical sessions”
Dr. Reza Parsamehr, Security Team Manager, Aumovio Engineering Solutions – Portugal

“The event was exceptionally well-organized and flawless in every detail—from the choice of venue to the lectures and themes”
Leticia Freitas, GRC, Randstad – Portugal

“CISO 360 Global Congress is **the** congress for CISOs and senior cybersecurity practitioners to attend. The scope of topics presented is excellent!”
CISO, DPO and Director of the Internal Control Office, Comissao do Mercado de Valores Mobilia¡rios, Portugal

“Refreshing views of security topics for knowledge improvement!”
CISO, Bank Credibom (Portugal)

“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”
CSO, Logista Portugal

“What I like about this CISO 360 conference is the peer interaction, the themes that we discuss here that are very relevant, the chance to speak openly in a way that you know that people will understand your problems and give you ideas. You can give something back and contribute to what could be the global outcome of the conference. It’s a sum of all the contributions, both people that do the presentations, the questions, the comments that we make. These things are all relevant, the speakers are well chosen, they are respected professionals on their fields, and the organisation is top, and the venue is always very beautiful place, everything is well organised so it’s highly recommended. Every time I attend CISO 360, I meet new people, there are faces that I see from year to year, some well-known. You see people from Asia, from America, from Europe, it’s mainly a European event but you see people coming from other continents, and it’s a very friendly modern atmosphere where people are at ease, everyone respects each other and we know that we can trust these people, we can share our problems, the questions we have, and there’s someone that went through the same thing and can give us an idea of what to do. I’m leaving with lots of new ideas for things that I want to implement and experiment, so that’s why I came, and that’s why people should come to these conferences, it’s great.”
Director of the Internal Control Office, Comissão do Mercado de Valores Mobiliários

“It seemed like everything was perfectly set to ensure a smooth event gathering 100+ valued guests. Loved the energy, the talks, the stands and also the choice of networking activities!”
CISO, Engie (France)

“CISO 360 is the perfect balance between working, socialising, and networking. So the appealing thing about coming here is you get to meet a load of people that you wouldn’t normally get in front of, so there’s some smaller vendors who if you Google certain area they’re probably not going to come up in the first page and you get to meet them and they get to tell you about their interesting new take on the technology, and you get to do it in a really nice setting, it’s a lovely hotel, the events that Pulse put on outside of the hotel are really good, where you get to socialise with people and after a couple of drinks they kind of tell you a bit more truthfully what their products can do which is really, really useful. And then you get to do the follow-on, the boring stuff where they take you through a slide deck in London afterwards, so you get to meet them properly first, and then learn about the bumph that they’ve got from their sales team afterwards so that’s really cool.”
Security Operations Manager, Right Move

“The CISO 360 Congress provided a unique platform to explore the delicate balance between innovation and practical implementation in cybersecurity. As a startup founder, I found the discussions on DevSecOps challenges and the evolving role of CISOs particularly enlightening. One key takeaway was the constant tension between designing for scale and the risk of over-engineering. In the startup world, we must be agile, forward-thinking, and grounded in current market needs. The debates around Generative AI highlighted this balance perfectly. These events are crucial for widening our horizons and engaging in insightful discussions with peers. They remind us that while pushing the boundaries of technology, we must always keep sight of the practical challenges security leaders face in their day-to-day operations. This blend of innovation and practicality will drive our industry forward.”
CTO and Co-Founder, JIT (Israel)

“As a newcomer to the cybersecurity event scene, CISO 360 was an eye-opener. I expected a highly technical environment but instead found a deeply human-centric experience. It revealed the true challenges and struggles that CISOs face daily. This insight is invaluable for someone in my role, as it helps bridge the gap between our products and the real-world needs of security leaders. The event’s structure, starting with a candid roundtable discussion, set the tone for the entire conference. It allowed us to view subsequent presentations and discussions through the lens of solving real problems.”
Regional Executive, KnowBe4 (The Netherlands)

“Great conference!  From the beginning, the level of participant engagement was very high.  The content was very informative and the presenters very knowledgeable.  Every aspect of Global CISO 360 was extraordinarily well done.  I left the event with a better understanding of cybersecurity and a broader network of industry contacts.”
Senior Director Security, Atlas Air (United States)

“Extremely insightful talks and a great way to connect with others in the industry that fostered genuine and open discussions”
Cyber and Geopolitical Risk lead, Sibylline (UK)

“Superb line-up of speakers and topics! The sequence of the ’roundtable’ at beginning, prior to ‘sitting down’ at the conference, was a very good ‘icebreaker’, socially, and this allowed us to get to know one another well.  Content and organization made this an excellent event!”
CISO, Infopercept (UK)

“A great experience – I liked the fact that the Pulse team had the energy to support and make this such an experience – everyone was friendly and there to support when needed”
Senior Account Executive, Hack the Box (Greece)       

“One of the biggest challenges in our industry is gaining access to open conversations with CISOs without prior introductions. Cold calling and traditional outreach methods often fall short. However, events like CISO 360 create an environment where everyone is approachable, solving this challenge elegantly. The casual atmosphere fosters open dialogue, allowing us to understand CISOs’ current challenges and how we can help. It’s not just about selling; it’s about building meaningful connections. These events provide a unique opportunity to engage in positive conversations and establish good relationships that lead to fruitful collaborations.”
GemServ, a Talan Group company (UK)

“As vendors, we’re often seen as just another salesperson despite our genuine desire to help improve the industry. Events like CISO 360 are invaluable for fostering connections. They open doors to future introductions, lunches, and even inclusion in specialised groups. These connections are the foundation of true industry collaboration. Interestingly, the most effective collaboration often happens off the record – in WhatsApp groups, over coffee, or during casual lunches. These spaces allow security professionals to share challenges without fear of oversharing or repercussions. To truly advance our industry, we need to encourage more of these human-to-human interactions.”
COO, Risk Ledger (UK)

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”
CTO, Quod Orbis

“One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive).”
CISO & DPO, 360 Treasury Systems AG, Germany

“A very thoughtful event, great networking and industrial expertise in the room to learn from!”
Director, Security, Laureate International Universities Malaysia

“A meticulous and engaging event highlighting the key security concerns business leaders face today!”
Director, Bestman Solutions

“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.” –
CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.”
CMO, SailPoint

“Insights and experience shared by industry leaders will definitely help me and my organisation in course correcting the strategy”
Senior Cybersecurity, Lafarge Holcim

“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.”
CEO, Cordery

“Once you attend CISO 360, you become a part of the family. The socialising offered is the most important aspect. This community building through shared experiences makes it different from other conferences!”
CISO, Head of Information Security and Assurance Services ILO – United Nations, Switzerland

“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.”
Global Deputy CISO, Cushman & Wakefield

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”
Chief Scientist and SVP of AI, Dataminr

“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to Sara, Clive and the team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good. Afterwards the meal sponsored by Qualys was fantastic. These are the smallest things that Pulse do for individuals such as myself that they don’t need to do, but they go out of their way just to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”
VP Information Security EMEA, Northern Trust

“It’s probably one of the best conferences for cybersecurity professionals. We really get to exchange information with other professors and peers in this industry, we build trust among us in this inclusive environment. We can exchange not only challenges, but celebrate the successes as well. And I would come back any time. We build not only trust and become friends, but also become part of the family. For CISOs it’s one of the most important things. Everybody expects CISOs to be very technical, and we are, but I believe that being very good on the soft skills is vital as well, and building that network is one of the most important things because CISOs cannot work alone. It’s almost impossible that you will know every single answer, so the networking is probably the most important thing in our field to pick up the phone, to say: “Hey, are you having the same challenge, how are you doing things around these problems or issues?” It really does help, and it’s proven itself over and over again. I use the CISO 360 network and call people. Besides information sharing, besides the fact that we all have become friends and family here, I would say we also have great evening events, which is how we build a stronger connection. CISO 360 is the place to be. I recommend it to all of our professionals in cybersecurity.”
CISO European Investment Bank

“This is a very good event for meeting CISOs, security professionals, and the vendors to learn more about what is going on, their challenges, and how to deal with them. This event has a number of really amazing speakers. Some of them have been in this industry for a long, long, long time, they have a broad variety of experiences, they share these experiences and they are still today trying to learn the next thing. There are three big benefits to attending CISO 360. The networking is one. You need to be able to share what you know and learn from others. The content from the stage is a second one, obviously, and the third one is the social aspect. We have a boat trip and wine tasting. Work is fine, but you also need to be personal, you need to bring those connections in because you never know when you need to pick up that phone and say: “Hey, I have this issue, I don’t know who to discuss it with, but I trust you.”
CEO and Founder, Praxis Security

“Thank you for the excellent event and seamless organisation! It was my first time at the CISO 360 and the event was highly inspiring with great networking opportunities.”
Senior Consultant, DHC AG (Switzerland)

“We’ve been with Pulse and the CISO 360 since it started, and it’s been an amazing journey and we’ve created this community and this family, we see new faces, the same faces. And one of the issues we have in our industry is the lack of communication, the lack of talking, so these events are bringing people, bringing our peers out to have those talks, it’s great for vendors, it’s great for the community. If another vendor is thinking about joining this community do it. There is a fantastic community. We get to talk between the vendors as well, meet new people, see old friends, and how they are progressing through the industry as well – they may have moved, gone to new roles, new jobs, new organisations, and it’s great to see them transitioning. So we learn an awful lot as well as the customers do from learning from what we have as a vendor. We talk about diversity an awful lot in this industry and I think Pulse has managed to grab that with its agenda and its itinerary, there is something for everybody throughout the two days, through the day and through the evening as well and I think that’s one of the reasons why it captures such a wide range of audience, it’s because we are talking about so many different topics that are burning, these are topics that customers and vendors are having internally, so Pulse is giving you the opportunity to bring them out and allow people to talk about them.”
CTO UK, Qualys

“It’s a really cool event, a lot of CISOs come to these events and it’s quite a small little community where they all do a lot of learning and a lot of conversations. As a start-up, CISO 360 is a great way to meet people and build relationships within the industry. As a start-up, we don’t have the marketing budgets of big companies, so for us relationships are really important, we need to build trust with the CISOs, they need to trust us before using our products, and that was a really great way to come to an event like this, meet CISOs, teach them a bit about what we’re doing and what we’re trying to achieve with our mission and then from there hopefully get a few using the product. Gather feedback on our products has been really good for two reasons, firstly we’ve got a lot of constructive feedback on what we’re doing, what we’re trying to achieve, and actually new ways which we can achieve that, and secondly we’ve got a lot of people who are willing to try the product and actually join the trial and get using it. It’s a very well organised event with really friendly people. It’s always a great venue as well – they rotate it around different cities and it’s always nice to come to a different part of the world and meet people in a setting that’s not London.”
CEO, Risk Ledger

“I keep coming back to CISO 360, because I learn so much. There is such a breadth of information, people from right across all sorts of industries, and organisational titles. The breadth of the agenda is just amazing, and it’s really fascinating, and so I keep coming back because I want more. I’ve learned so much in the last couple of days about all sorts of different topics, from the really scary from Dr. Sally Leivesley’s presentation to areas about recruiting people, and what makes up a good team, and data governance. There is such a plethora of information, it’s impossible to do without CISO 360, so I come back for more – and I’ll be back next year. I think the atmosphere in this group is really open, it’s very friendly, they’re very welcoming. We like people, we talk to people, and nobody was left alone at the networking events. It’s a very inclusive group, and we welcome new people coming along because we want new experiences, we want to talk to new people. The really good thing about this group is that you can come along and have a really easy conversation about information security, cybersecurity, anything to do with security because this is a really knowledgeable audience, and it makes it easy and it’s very relaxed, you don’t have to fight anybody, everybody understands. It’s simply great.”
Head of Information Security, Quilter

“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.”
Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, United Kingdom

“What a week! Such a lovely venue, lovely city, and a fantastic collective of like-minded professionals. This was my first Annual CISO Congress, but not my first Pulse event, and Pulse did not fail to deliver their exceptional services once again. Sara and the team did a wonderful job, and pulled everything off brilliantly.”
Threat and Vulnerability Consultant, Computacenter, United Kingdom

“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way. The Pulse Conferences team puts this together from the heart.”
CISO, HARIBO (Germany)

“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.”
Information Security Compliance and Assurance Director, Flight Centre UK

“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”
Europe Industries- Security Officer, Air Liquide GMS (France)

“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.”
Director, Resilient World

“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.”
Technology Services Head of Cyber Security, DWP (UK)

“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the CISO 360 Congress. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.”
Peter Wood, Naturally Cyber LLP

“Excellent conference”
Barbara Aung, CISO, Telefonica

“This was great, we have a lot of good take away’s and loved the lessons learned!”
Sybil Kleinmichel, 360 Treasury Systems AG

“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting”
CMO, Vectra

“If you want to hear real CISO experiences, you must attend this event!”
CISO, ST Engineering, Singapore

“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC

“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.”
CMO, NetClean

“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!”
Senior Manager, Cybersecurity, EY Singapore

“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!”
Chief Privacy Officer, Nokia Group

“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.”
CMO, SailPoint

“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!”
Group CISO and Group DPO, MS Amlin

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.”
CMO, Synack

“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.”
CMO, Telstra

“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ”
Supporting Organisation, ClubCISO

“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”,
President, (ISC)2 Scotland Chapter

“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape”
GRC Specialist, Euronext

“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!”
CISO, GOPA International Energy (Abu Dhabi)

“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin

“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”,
Director Security Engineering, Inmarsat

“A very engaging, varied and interactive event. The best conference I have ever attended!”
Information Security Manager, Lloyd’s of London

“The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government

“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”
CISO, Channel 4

“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ”
Director Sales, Sailpoint

“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA

CISO 360 Congress created a strong platform for peer review, cross pollination of idea and networking.”
CISO, Gebauer & Griller

“Pulse Conferences stand out for being up to the minute with developments and concerns. First rate speakers and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum

“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Cygenta (USA)

“Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Cygenta (USA)

“Excellent conference, brilliantly put together.”
Director, Bridewell 

“Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall

“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!”
Director of Information Security EMEA, Canon Europe (UK)

“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!”
Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)

“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!”
Corporate Security Manager, Logista (Portugal)

“Marvellous event, well-run, packed with useful content you can use”,
Technology Services Head of Security, DWP

“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland

“I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV (Spain)

“Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv